
News · Breach Analysis · Breaking
Cyberattack on cloud provider Arcadia may expose data of 125,000 Japanese police officers and staff
A cyberattack on Osaka-based cloud provider Arcadia may have exposed names and email addresses of about 125,000 officers and staff across 20 Japanese prefectural police forces, plus more than 18,000 addresses registered for crime alerts.
Mark FermorCTO, CMO and Founder, Firevault
Published 21 October 2026 · 3 min read
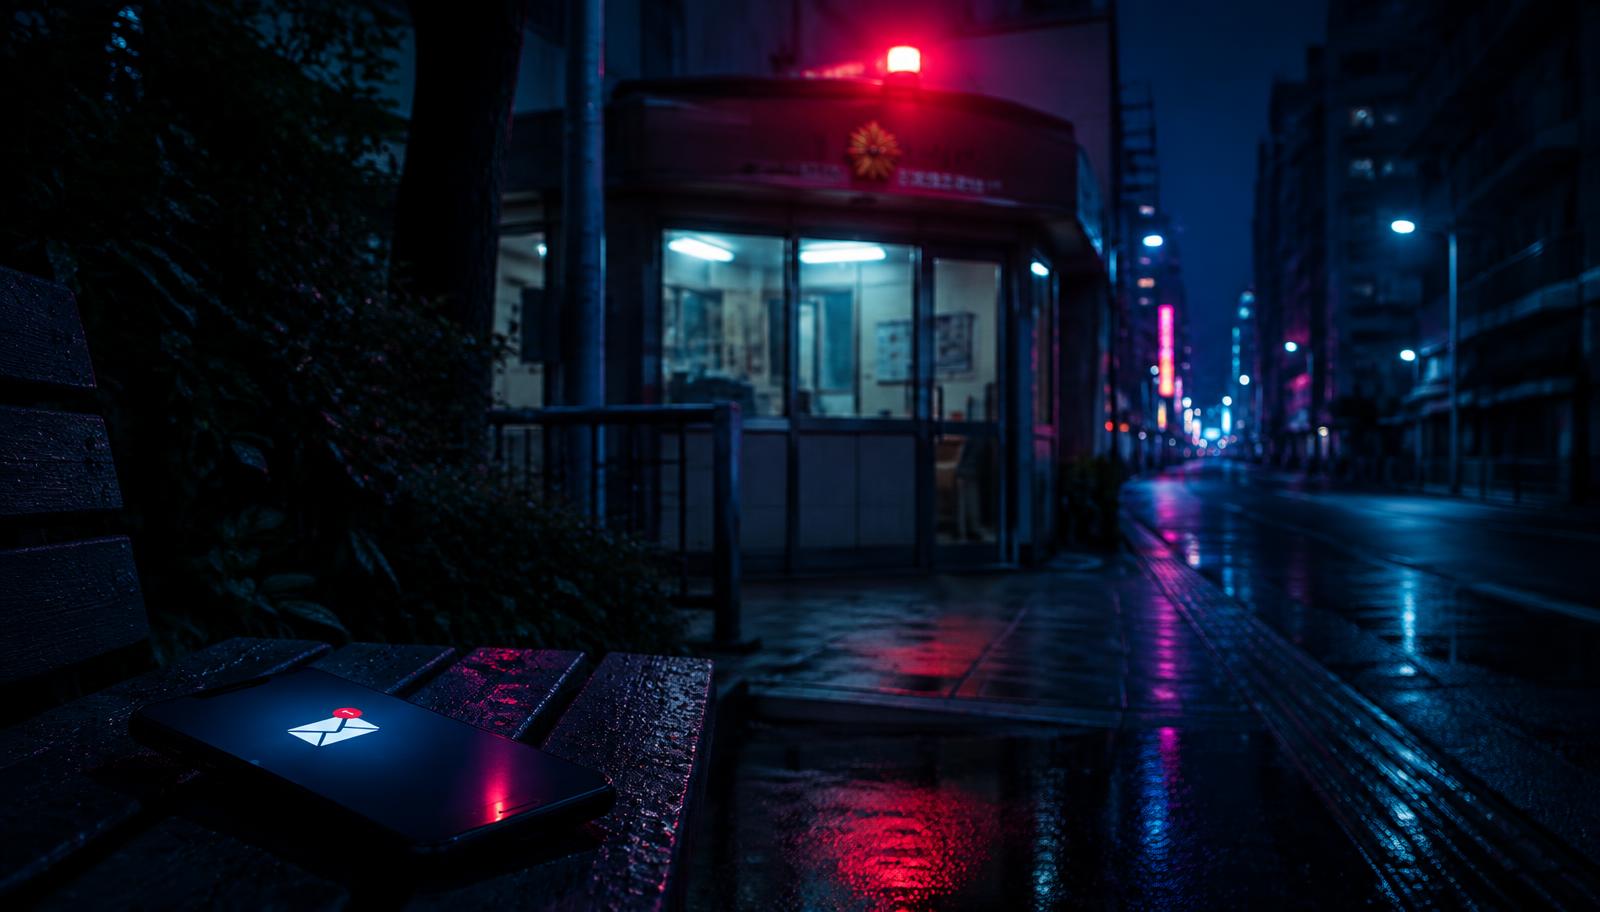
A Japanese police box at night on a wet street, with a smartphone showing an email notification on a bench
What happened
Personal information belonging to about 125,000 officers and staff members at 20 prefectural police forces in Japan may have been compromised in a cyberattack on cloud service provider Arcadia, according to sources at the National Police Agency (NPA) cited by Jiji Press and The Japan Times on 21 October 2026.
The 20 forces, including those in Aichi, Hyogo and Hiroshima prefectures, had outsourced to Arcadia, which is based in Minoh, Osaka Prefecture, a system used during emergencies such as natural disasters to check whether personnel were safe and able to report for duty.
What data may be affected
- Names and email addresses registered with the emergency safety check system. Because the system was built for emergency contact, most addresses are believed to be personal accounts used on private mobile phones.
- Department details for some forces, including Tochigi and Saitama, which had also recorded which department employees work in.
- Crime alert subscribers. Four forces, including Shimane and Yamaguchi, also used Arcadia to send crime alerts. Those systems held the names and email addresses of about 16,000 individuals and more than 2,600 email addresses of companies and other organisations.
Kyoto and Fukuoka prefectural police used both systems.
The response so far
No misuse of the information for fraud or other crimes has been confirmed, the sources said. The NPA has told affected forces to gather information, warn people about the risk of further harm and arrange alternative ways of contacting personnel in an emergency.
The attack has also raised concern about possible exposure at other Arcadia customers, including local governments and fire departments across Japan.
Why this matters
This is a supplier incident, not a breach of police networks themselves. One provider serving many public bodies became a single point of exposure for all of them. The data involved is also sensitive in context: personal contact details for police personnel can be used for targeted phishing or harassment.
There is a second consequence. An emergency contact system that cannot be trusted has to be replaced at short notice, which is exactly what the NPA has now asked forces to do.
Points for organisations to consider
- Know which suppliers hold your staff and customer data, and what each one holds.
- Keep contact lists and other records you would need during an incident available in a copy you control, outside the supplier's environment.
- Plan an alternative way to reach people if a hosted communication service is unavailable or compromised.
Offline Secure Storage® from Firevault keeps a dedicated copy of critical records physically disconnected by default, reachable only through an authorised, identity-verified session. It does not prevent a supplier being attacked, but it means the copy you depend on is not sitting on a permanently connected network.
Source: The Japan Times, translated from Jiji Press, "Data breach potentially exposes information of 125,000 police officers and staff", 21 October 2026. Details are attributed to NPA sources and have not been independently confirmed by Firevault.
Questions
About 125,000 officers and staff across 20 prefectural police forces, plus about 16,000 individuals and more than 2,600 organisations registered for crime alerts, according to NPA sources.
Mainly names and email addresses, many of them personal accounts, and for some forces the department in which employees work.
No misuse had been confirmed as of 21 October 2026, according to the NPA sources cited.
Sources and reporting notes
- japantimes.co.jpPrimary reporting referenced in this analysis.
Incident facts are attributed to the named sources; the recommendations and product discussion are Firevault analysis by Mark Fermor.
About the author
Mark FermorCTO, CMO and Founder of Firevault. Mark writes on physical control, offline storage and the incidents that show why both matter.
Why #OSS
Keep a clean copy out of reach.
Offline Secure Storage® keeps one copy physically disconnected at the hardware level between sessions.
Control
Govern the paths attackers depend on.
Physical, out-of-band control of selected network paths, composed into ten Blueprints.
Ready to start?
Create your Vault online.
Business Vaults from £360 a month inc VAT, on a 36-month commitment.