
News · Breach Analysis
EY data breach: client tax records exposed through a support platform
Client tax documents held in EY support tickets were downloaded by an unauthorised third party. Later reports link the exposure to Goldman Sachs, Man Group and Tishman Speyer.
Mark FermorCTO, CMO and Founder, Firevault
Published 15 October 2026 · 7 min read
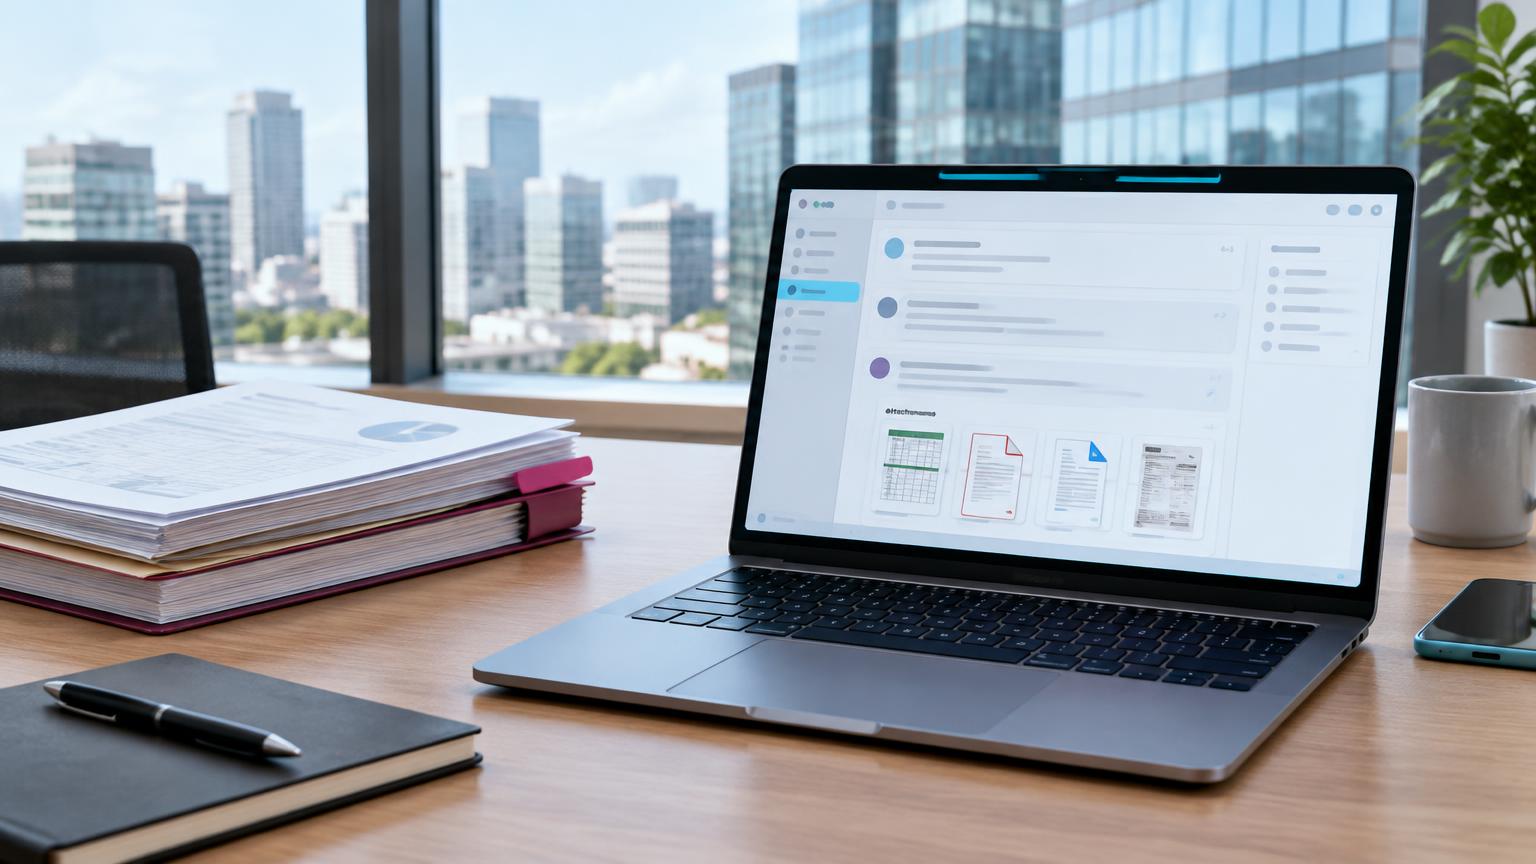
Conceptual editorial artwork of client financial documents beside a laptop showing support-ticket attachments; not an image of EY systems
Sensitive client records do not always stay inside the systems designed to hold them. A tax document attached to a support ticket can become another copy, with different access controls and a different route out of the business.
That is the central lesson of the EY breach. Ernst & Young LLP confirmed that an unauthorised third party downloaded documents from a third-party IT support platform earlier this year. October reporting has linked the incident to information belonging to clients of Goldman Sachs’ wealth management business, Man Group and Tishman Speyer.
This is a client-confidentiality incident, not evidence that those organisations’ own networks were breached. Goldman Sachs said its systems were unaffected and client assets remained safe. Man Group also said its systems were not compromised.
Reporting cut-off: 15 October 2026. This article draws on EY’s official notification and the supplied Cybersecurity Intelligence report. The accompanying image is original conceptual artwork, not a photograph of EY’s systems or evidence from the incident.
What EY has confirmed
In its notification dated 13 July 2026, filed with the California Attorney General, EY described a third-party information technology service management platform used by its IT personnel to support teams carrying out tax-related work.
Support tickets submitted through that platform could include documents containing client tax information. EY said an unauthorised third party accessed the platform between 28 March and 12 April 2026 and downloaded documents relating to a number of clients.
EY identified anomalous activity on 23 April 2026, eleven days after the end of the reported access window. Its information security team began incident response, and an independent cyber security firm assisted the investigation. EY said the unauthorised access had been stopped and the systems were secure.
The letter also said federal law enforcement had been notified. At the time of that notification, EY said it was not aware of misuse or further exposure of the affected personal information, or evidence that particular individuals had been specifically targeted. Those were findings at that point in the investigation, not assurances that stolen information could never be misused.
Why the client impact has widened
The 12 October Cybersecurity Intelligence report describes letters sent to clients in late September and links the exposure to Goldman Sachs’ wealth management business, Man Group and Tishman Speyer.
The report says exposed information included names, addresses, email addresses, tax identification numbers and financial details. EY’s publicly available July notification is a sample letter: its individual data-element field is a placeholder. It confirms that financial information contained in, or used to prepare, tax filings was involved, but it should not be read as a complete list of fields exposed for every person.
The distinction matters. The practical question for an affected client is not whether every possible data field appears in a headline. It is which of their own documents were involved, what those documents contained and what support is being offered.
For financial institutions, the incident also creates a responsibility to explain an exposure that happened at an external adviser rather than inside their own network.
A support ticket became a sensitive record store
The affected platform was a support system, not simply the main repository for tax work.
Attachments help staff explain faults and resolve problems. But when those attachments contain complete client records, a helpdesk can accumulate its own collection of sensitive information. Closing a ticket does not necessarily remove its attachments, and securing the original record does not automatically secure every later copy.
That is how an apparently routine workflow can extend the reach of a breach. An attacker who reaches a support platform may find information belonging to people and organisations who never used that platform directly.
The lesson is not that support tickets should never have attachments. It is that sensitive attachments need a clear purpose, limited access, an appropriate retention period and a documented way to remove them when the support task is complete.
What remains uncertain
Cybersecurity Intelligence reports that EY attributed the incident to a vulnerability in Checkmarx software. However, the sources reviewed do not establish a specific vulnerability identifier, affected version or complete exploit chain. EY’s July notification does not name the software vendor.
It would therefore be premature to turn that attribution into a detailed technical account of how the attacker entered the platform.
The reviewed sources also do not establish a final total of affected people or the full number of downloaded documents. Nor do they demonstrate a compromise of Goldman Sachs’ or Man Group’s internal systems. Client-data exposure and a direct network breach are different events and should not be conflated.
What affected clients can do
Start with the notification sent by the institution or adviser responsible for your records. Ask which documents were affected and whether tax identifiers, financial account details or other information that could support impersonation were involved.
Use a known contact number or the institution’s usual website to verify unexpected messages. Information taken from tax records can make a fraudulent email or call sound unusually convincing. Do not assume that someone who knows your address or investment details is entitled to instruct a payment or request further documents.
EY’s July sample notice offered eligible individuals 24 months of Experian credit and identity monitoring, together with identity restoration support. Eligibility and enrolment instructions should be checked against each person’s own letter rather than copied from a public sample.
What boards and professional firms should ask
A supplier review needs to go beyond the system where the client record starts. Ask where copies end up during support, testing, troubleshooting and incident response.
- Which support platforms can hold client documents?
- Can staff provide a redacted extract instead of a complete file?
- Who can access attachments, including supplier personnel?
- How long are attachments retained after a ticket closes?
- Can the firm identify every affected client if those attachments are taken?
- What independent evidence supports a supplier’s claim that remediation is complete?
Cybersecurity Intelligence reports that Goldman Sachs’ technology risk team requested objective evidence and third-party checks of EY’s remediation. The report specifically attributes that request to Goldman Sachs; it does not establish that every affected organisation made the same demand.
Protecting important records without overstating the answer
Offline Secure Storage® addresses a separate but complementary requirement: keeping an important retained copy physically disconnected when it is not in use. Using OSS means an organisation can protect that copy from a continuously connected access path.
It does not recover confidentiality once another copy has been stolen, secure a supplier’s helpdesk or make it safe to attach unrestricted client files to a ticket. Data minimisation, controlled access and supplier assurance remain necessary.
The EY incident is a reminder to protect both the record that matters and the everyday workflow that makes another copy of it.
Sources
- EY: official notice of data breach, dated 13 July 2026. Primary source for the access window, detection date, support-platform description and response.
- Cybersecurity Intelligence: Ernst & Young Breach Exposes Clients, 12 October 2026. Source supplied for this article, including later client notifications and institutional responses.
- Bloomberg Law: Goldman Sachs ensnared in EY data breach earlier this year. Further reporting linked by the supplied source.
By Mark Fermor, CTO, CMO & Founder, Firevault.
Questions
The supplied report says Goldman Sachs stated its systems were unaffected and client assets remained safe. Man Group also said its systems were not compromised. The exposure involved a platform used by EY.
EY’s official notification says an unauthorised third party accessed the platform between 28 March and 12 April 2026. EY detected anomalous activity on 23 April 2026.
No. A physically disconnected retained copy can reduce that copy’s network exposure, but it cannot undo theft from a supplier’s support system or protect every other copy of a document.
About the author
Mark FermorCTO, CMO and Founder of Firevault. Mark writes on physical control, offline storage and the incidents that show why both matter.
Why #OSS
Keep a clean copy out of reach.
Offline Secure Storage® keeps one copy physically disconnected at the hardware level between sessions.
Control
Govern the paths attackers depend on.
Physical, out-of-band control of selected network paths, composed into ten Blueprints.
Ready to start?
Create your Vault online.
Business Vaults from £360 a month inc VAT, on a 36-month commitment.