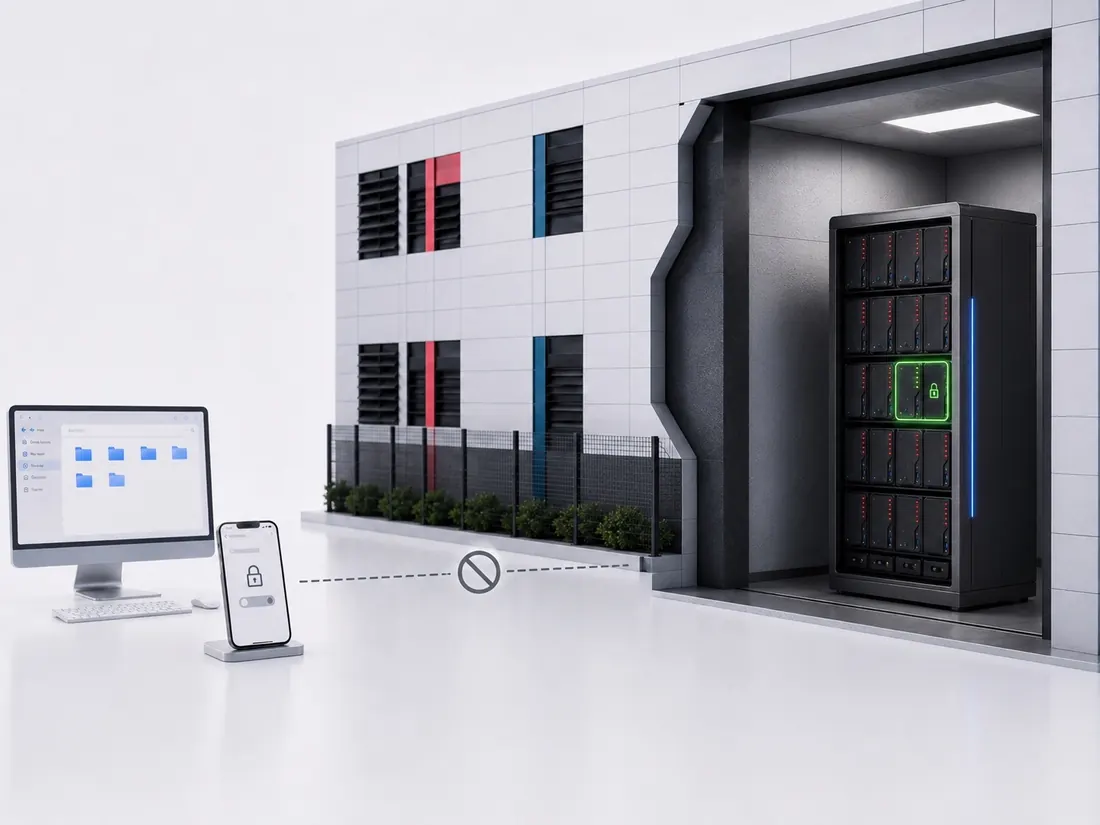
Firevault, offline secure storage, physically disconnected from the internet
Pricing

Enterprise product iconEnterpriseEnterprise-grade offline secure storage™

The bigger the estate, the more routes into it.

Sites, systems and suppliers, all connected. One compromised route can reach the recovery copies a whole organisation depends on. Enterprise keeps that copy offline, on dedicated hardware, with no standing route to it.

From 300TB. Delivered as a programme, with a named account manager and technical lead.

One supplier connectionDay 1, 06:00

  • Supplier remote accessTrusted and always onReachable
  • Management networkShared with operationsReachable
  • Every connected siteJoined to the same estateReachable
  • Backups and replicasManaged from the same networkReachable
  • Firevault EnterpriseNo standing routeOffline

One route led to all of it. Enterprise had no standing route to follow.

What happens when

At this scale, disruption is measured in weeks.

Large estates are rarely breached head on. Attackers come in through a trusted route, then move to the systems that run everything else.

  1. A supplier is compromised.

    An attacker gets into a trusted supplier that has remote access to your estate.

  2. The management network is reached.

    From there, the systems that run your sites, and the backups behind them, are in reach.

  3. Still recovering.

    Operations are disrupted while every system is rebuilt and shown to be clean.

Recovery is slow when every copy is suspect. It starts with one that was out of reach.

See recent breaches
  • 2025Jaguar Land Rover: production stopped for around five weeks
  • 2025Collins Aerospace: check-in disrupted at several European airports

What Enterprise is

A physically offline copy of your estate’s critical data.

Enterprise is Offline Secure Storage® at the scale of a whole estate: dedicated hardware, in your facilities or ours, that stays offline unless an authorised session is open.

Enterprise is a physically offline copy of your estate’s critical data, with no standing route to it.

  • No standing route

    The network path exists only for an authorised session, then it is removed.

  • Managed out of band

    The management plane is physically separated from the data plane, so it never shares a path with the archive.

  • Yours alone

    Purpose-built arrays commissioned for your organisation, in your facilities, a Firevault Bunker or both.

What it changes

Weeks of uncertainty, or a clean place to start.

Enterprise does not stop every incident. It means the copy you recover from was never part of it.

Estate recoveryWeek 1
  • Operational networkUnder investigation
  • Primary backupsNot trusted
  • Enterprise archiveClean, offline
  • Priority sitesRestoring
Sessions loggedIdentity checksEvidence exported

Recover the estate from a copy that was out of reach.

  • A clean, sovereign copy with no standing route from the compromised network
  • Recovery that can start with the sites and services that matter most
  • Evidence of every session and identity check, for your board, regulators and insurers
  • Custody and jurisdiction you choose: your facilities, a Firevault Bunker or both
Book a scoping call

Could that be you?

Different sectors. The same question.

What happens to the recovery copy when the estate around it is compromised?

Switch between the two endings.

ExposedDay 1, 06:00

An energy network operatorCISO, national infrastructure

The moment

A supplier’s remote access has been used against you.

Operational records and recovery images sit on storage the management network can reach.

Recovery waits on every system.

Nothing can be restored until each copy is shown to be clean.

A clean copy, held offline.

The recovery images were in Enterprise, with no standing route from the compromised network.

ExposedWednesday, 11:30

A government departmentDirector of digital

The moment

An attacker is inside the shared estate.

Sensitive holdings and the backups behind them are managed from the same network as everything else.

Every connected copy is in question.

The department has to assume anything reachable has been seen or changed.

The holdings were out of reach.

They sit in Enterprise in the department’s own facilities, managed out of band.

ExposedBoard meeting

A bankHead of operational resilience

The moment

The board asks how you would recover from a severe attack.

Every recovery option on the list shares a route with the systems it protects.

The answer is another connected copy.

It is hard to show the board a copy an attacker could not reach.

The answer is an offline gold copy.

Enterprise holds it, with every session and identity check logged as evidence.

These situations are illustrative.

Who Enterprise is for

Critical national infrastructureEnergy, water, telecoms and transport

Recovery copies and operational records for services the country relies on.

Defence and governmentSovereign programmes

Classified holdings and sovereign data, with cleared people where required.

Large enterprises300TB and beyond

Sensitive data at a scale that spans sites, teams and jurisdictions.

Regulated industriesBanking, healthcare and legal

Records you must protect, retain and be able to evidence.

Available today

Delivered as a programme. Supported for its life.

Enterprise is more than hardware. Each programme is engineered for your estate and supported by a named team that knows it.

Deployment engineering

Site survey, rack design, power and cooling, commissioning and handover.

Multi-site architecture

Capacity split across your facilities and Firevault Bunkers.

Custom integration

API, SFTP and bespoke pathways into your environment.

Evidence and reporting

Connections and identity checks logged and exportable for SIEM, audit and insurers.

A named account team

An account manager and technical lead for the life of the programme.

Growth without migration

Capacity added in 20TB blocks, with no migration as you grow.

Included with every instance

  • 24/7 on-demand access
  • File Manager
  • File Share
  • Vault Buddy
  • Hardware return: renew, retrieve, or destroy the media with a certificate

Enterprise or Storage

Feature Enterprise Storage
Capacity 300TB and beyond, in 20TB blocks 20TB to 300TB, in 20TB blocks
Default state Physically disconnected Physically disconnected
Hardware Purpose-built, dedicated arrays Dedicated hardware
Where it lives Your facilities, a Firevault Bunker or a customer-scoped hybrid across sites A Firevault Bunker, your premises or hybrid
Management Out-of-band management plane, physically separated from the data plane Out-of-band window control
Engineering Site survey, rack design, power, cooling and commissioning Designed with our solutions team
People Named account manager and technical lead. Personnel and clearance requirements agreed during scoping Our solutions team
Agreement A programme with bespoke SLAs and integration engineering A written proposal

Assurance, mapped to outcomes

  • CNI and NIS2Enterprise can help support resilience and recovery obligations for essential services.
  • ISO 27001 and GDPRControls mapped to the outcomes these frameworks ask you to evidence.
  • NCSC CAFMapping available on request.
  • Cyber Essentials PlusCurrent status and scope require confirmation with Firevault.

Protecting the paths, as well as the archive? Control the path. Protect the asset.

Control physically governs which network paths exist across IT and OT estates. Enterprise keeps the recovery copy out of reach. Control governs agreed network connections. Enterprise separately holds recovery copies.

Explore Control

How it works

No standing route. A window, then nothing.

A site asks for access. The control plane authorises it out of band. A transfer window opens, then the physical path is removed.

The architecture

Step through it, or let it play.

  • Out of bandThe control plane authorises sessions away from the data path.
  • Time boundA window opens for the job, and only for the job.
  • RemovedWhen it ends, the physical path is removed and the archive is offline again.

Fig. 1 · The architectureOut of band

A site requests access to the archive.

What it is made of

A Firevault Bunker with a storage cabinet open, the hardware assigned to one organisation
Purpose-built arrays

Commissioned for your organisation, not shared racks or virtualised partitions.

Physically disconnected

The network path exists only for an authorised session, then it is removed.

Out-of-band management

Separated from the drives, which removes a common route for lateral movement.

Hardware-level encryption

Hardware-level AES-256 encryption; transport protection agreed during design.

Your facilities, or ours

Installed and commissioned in your own secure sites, a Firevault Bunker, or both.

Cleared people

Personnel and clearance requirements agreed during scoping.

Where it lives: your sites, our Bunker, or a customer-scoped hybrid

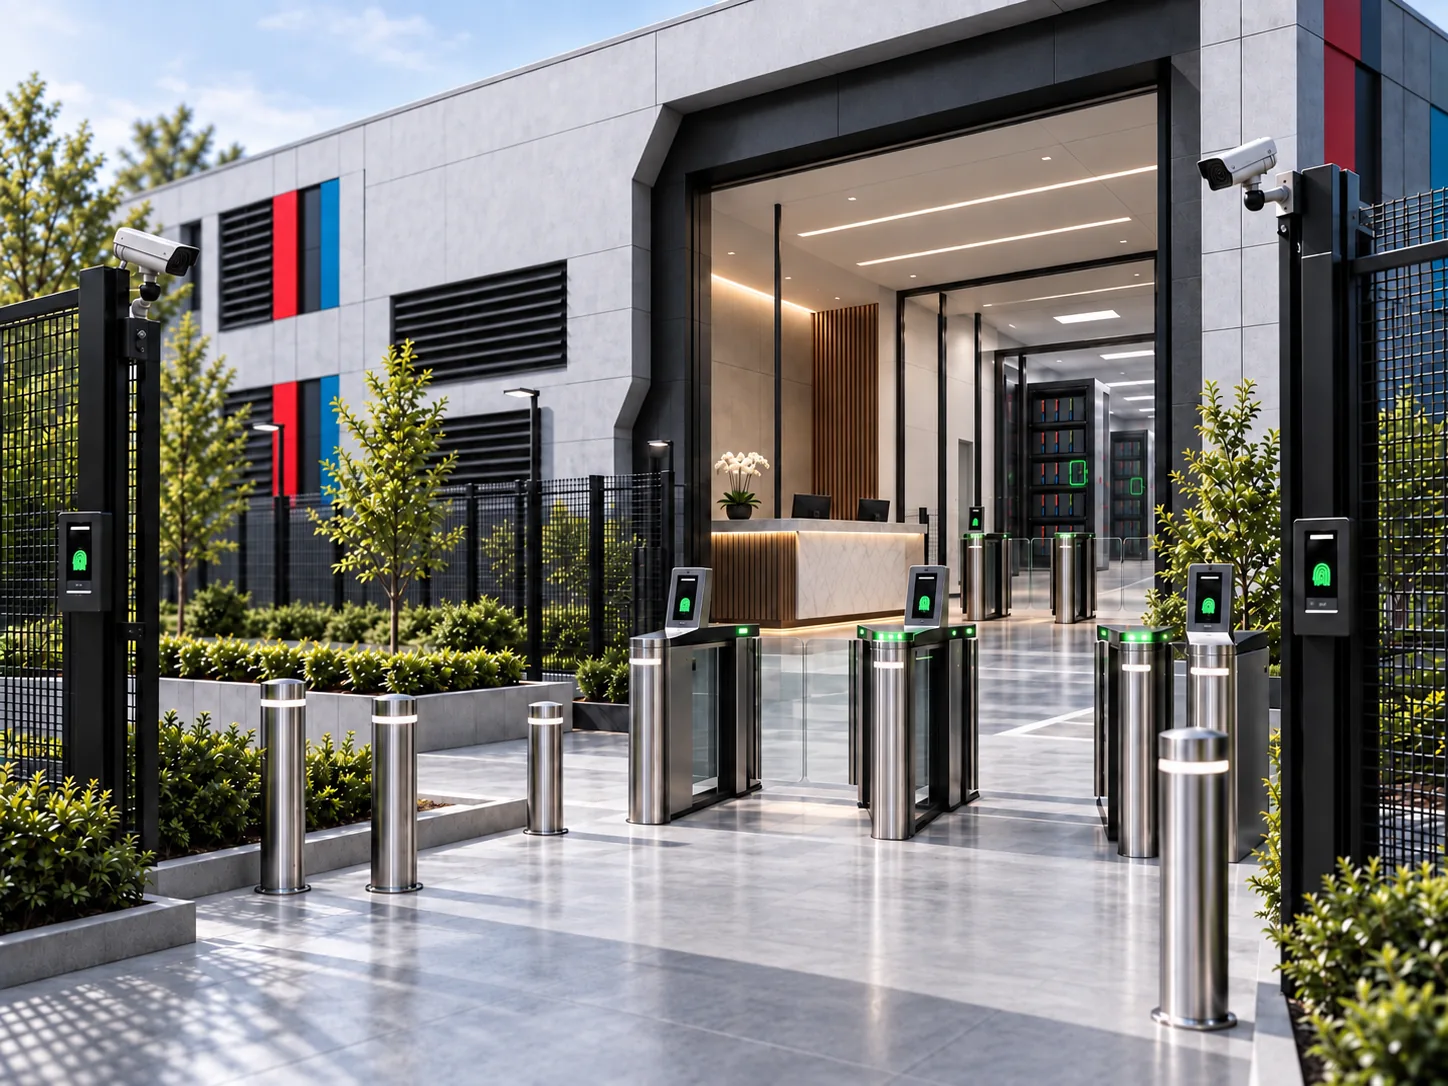
Secured Firevault Bunker entrance with biometric entry and monitored access
In a Firevault Bunker

Controlled entry and Firevault custody, in a facility separated from your operational network.

On your premises

The same hardware and disconnection, installed in your own secure facilities and under your custody.

customer-scoped hybrid

A working set on your sites, with the gold copy held in a Firevault Bunker.

How a programme runs

  1. Step 1Discovery

    The data you hold, expected growth, your obligations and clearance requirements.

  2. Step 2Site and survey

    Rack design, power, cooling and physical security for each location.

  3. Step 3Integration design

    Mapping to your backup, archive and operational technology workflows.

  4. Step 4Proposal and delivery

    Commissioning, handover, SLAs and support, set out in a written proposal.

Works with what you have

SFTP endpoint

Standard clients and ciphers, reachable only during an authorised window.

REST scheduling API

Schedule windows, list audit events and trigger emergency offline.

Your backup estate

The offline gold copy behind your primary and backup tiers.

Delegated access

Named individuals with defined rights over defined data sets.

For your technical teamThe full specification
Capacity
300TB and beyond, in 20TB blocks, with no migration as you grow
Hardware
Purpose-built, dedicated arrays commissioned for your organisation
Default state
Physically disconnected at the hardware level (Layer 1). No standing network route
Management
Out-of-band management plane, physically separated from the data plane
Encryption
Hardware-level AES-256 encryption; transport protection agreed during design
Deployment
Your facilities, a Firevault Bunker or a customer-scoped hybrid, across multiple sites
Integration
SFTP endpoint, REST scheduling API, backup estate integration and bespoke pathways
Evidence
Connections and identity checks logged and exportable for SIEM, audit and insurers
Included
24/7 on-demand access, File Manager, File Share, Vault Buddy
People
Named account manager and technical lead. Personnel and clearance requirements agreed during scoping
End of term
Renew, retrieve the hardware, or have the media destroyed with a certificate
Pricing
OSAP and OSSC, quoted against your estate in a written proposal
Sessions
Up to 120 minutes within the agreed access policy. Larger transfers are planned across authorised sessions.

Questions

Before you scope a programme.

Bring your infrastructure, security and continuity leads. We will take them through the architecture.

Can we buy Enterprise online?

No. Enterprise is consultation-led and delivered as a programme, priced in a written proposal against your estate. Vault and LUV can be bought online.

Will it change how our teams work?

No. Your live systems and backup tiers stay as they are. Enterprise sits behind them as the offline gold copy, and connects only for authorised windows.

Can it be installed in our own facilities?

Yes. Hardware can be installed and commissioned in your own secure facilities, in a Firevault Bunker, or across both.

How is the management plane protected?

It is physically separated from the data plane and runs out of band, so it does not share a route with the archive.

Do you provide cleared engineers?

Personnel and clearance requirements are agreed during scoping.

How is it priced?

On the same published model as Storage: Offline Secure Access Profiles for each named person, and Offline Secure Storage Capacity in 20TB blocks, quoted against your estate.

What happens at the end of the term?

You can renew, retrieve the hardware, or have the media destroyed with a certificate.

Your next step

Scope your programme.

Discovery covers the data you hold, expected growth, your obligations and clearance requirements.

Book a scoping call

Delivered as a programme, from 300TB.

Starting smaller? See Storage