Firevault, offline secure storage, physically disconnected from the internet
Pricing
Conceptual illustration of a connected office separated from protected storage

The company behind OSS and Control

About FirevaultPhysics, not promises.

Founded to challenge how we protect valuable information and critical infrastructure. We questioned the reliance on continuous connectivity and looked to physics for a different answer.

Protect what matters. Control what moves.

Our story · The challenge

We questioned the rules.
Then we set out to rewrite them.

For decades, cybersecurity has focused on stronger digital defences. More firewalls. More software. More monitoring. More encryption.

The technology, threats and investment have evolved. Yet organisations continue to lose valuable information and experience disruption that can take months or years to recover from.

We keep almost everything connected, then spend enormous amounts of money trying to stop people reaching it.

A different way of thinking

We thought there had to be a better way.

Why should our most valuable information remain connected when nobody needs it? Why should its protection depend entirely on software, passwords, encryption and active defences?

What happens when those defences fail, the systems managing them are compromised or the power goes out?

These were not questions about building another cybersecurity product. They were questions about changing the rules.

The breakthrough

Physics, not promises.

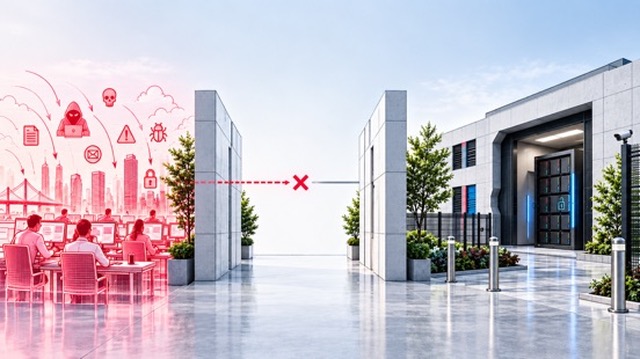
Instead of relying entirely on defending the path, why not remove the path when it is not needed?

An open physical connection.

A connection that is physically open cannot carry network traffic across that path.

No standing network route.

Physically disconnected storage removes the standing network route to that copy. An authorised session deliberately restores access.

Protection beyond software.

A secured physical environment protects the hardware beyond the software running inside it.

Isolation without power.

A correctly designed and verified fail-disconnected system can retain physical isolation when power is lost. This is a design condition, not a guarantee for every installation.

These are physical conditions that can be designed, controlled and verified, not claims that an attack will never happen. Controlling connectivity at Layer 1 complements good cybersecurity; it does not replace it.

What we built

From an idea to a new approach.

Founded in 2025 by Mark Fermor and David Bailey, Firevault brought together experience in technology, commercial strategy, business transformation and security.

We combined that experience with specialist knowledge in cybersecurity, defence-grade technology and critical infrastructure.

From the physical layer upwards

Change the conditions under which data can be reached.

We took conventional IP-connected storage apart and questioned how connectivity, access and data protection had become so tightly coupled.

We separated connectivity control from identity verification and data access, qualified specialist physical isolation technology and developed a platform that makes connectivity a controlled, authorised and time-bound event.

What began as an architectural idea progressed through laboratory testing into a live platform protecting real customer data. We did not set out to build another backup product.

The birth of Offline Secure Storage®

Physical storage, disconnected from the network by default and accessible through an authorised, identity-verified session. We call it Disconnect to Protect®.

Physical Control

We physically control the connection, rather than relying solely on software to restrict access. When an authorised session ends, the network path is removed.

Physical Storage

Vault, Storage and Enterprise provide dedicated customer hardware. LUV makes physical-first protection accessible through an isolated allocation on a shared instance.

Physical Security

Hardware is held within secured physical environments, whether hosted in specialist facilities or deployed on customer premises.

Physical Ownership

Customers have an identifiable storage allocation and clear control over their information, including access and what happens at the end of its service life.

Protection should not depend on the size of your organisation.

A solicitor preserving confidential records, a business securing recovery copies, a critical infrastructure operator protecting essential information and a family keeping important documents all hold assets they cannot afford to lose or expose.

Different capacities. Different operating requirements. The same physical-first philosophy.

The people and ambition

Built by people who believe there is a better way.

Mark Fermor and David Bailey lead Firevault as co-founders and equal partners, supported by an experienced technical team, specialist partners and advisers.

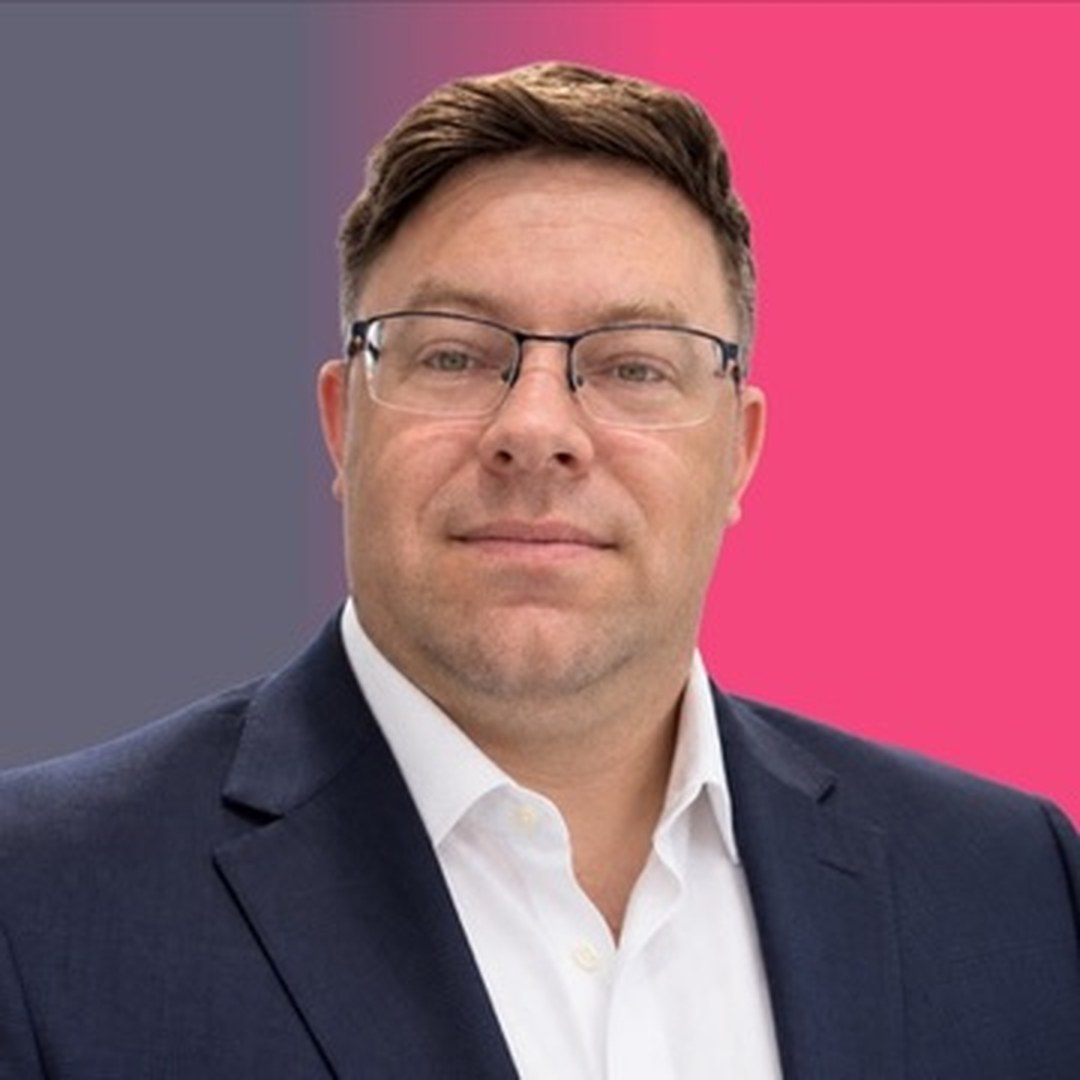
Mark Fermor

Mark Fermor

CTO, CMO & Founder

Mark brings more than 20 years of experience across technology, commercial development, product strategy and marketing, leading Firevault’s technology, security and brand direction.

LinkedIn
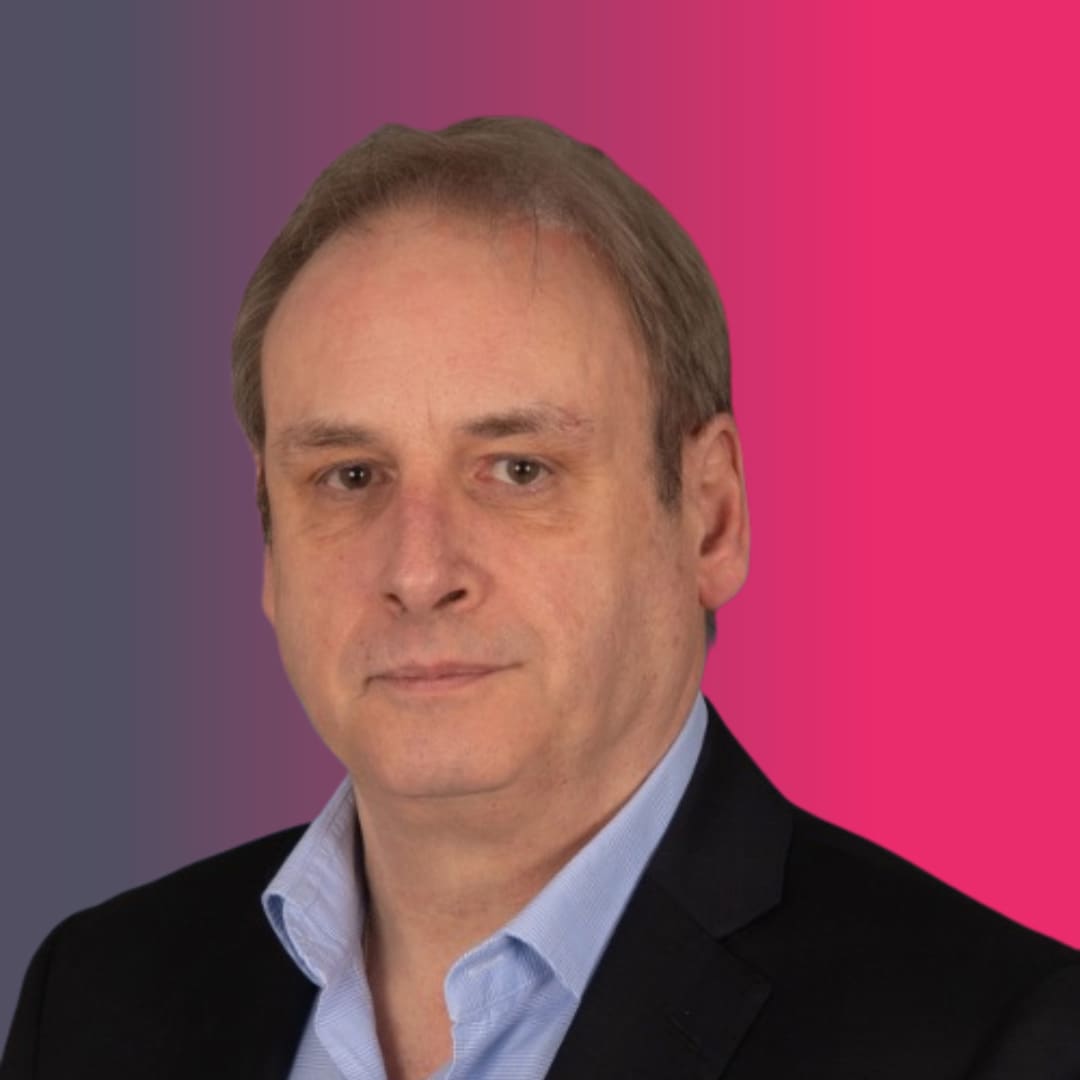
David Bailey

David Bailey

Co-Founder & CEO

David brings extensive experience in commercial leadership, finance, business growth and building organisations.

LinkedIn
Kenny Phipps

Kenny Phipps

Solutions Lead

Kenny’s cybersecurity experience helps translate complex customer requirements into practical architectures.

LinkedIn
Chris Priest

Chris Priest

Platform Lead

Chris brings more than two decades of global infrastructure experience to the systems behind Firevault.

Our thinking did not stop at storage.

Why should third-party access remain available when nobody is authorised to use it? Why should a compromised software control be the only barrier between an attacker and a critical system?

These questions led us to develop Control by Firevault: physical connectivity control for network access, system isolation, third-party connections and incident containment.

OSS protects valuable digital assets.

Storage protects selected copies between authorised sessions. It does not replace live working data, good security practice or tested recovery.

A human way to understand our collaboration

A check-up. A decision.
A path to recovery.

Like good medical care, cyber resilience brings together assessment, monitoring, a considered intervention and ongoing care. Different specialists. Clearly defined responsibilities.

In medical care

The check-up

A patient visits the doctor because something needs a closer look.

For your organisation

Firevault

Understand the situation

A CTO, CIO or COO starts a review of networks, critical national infrastructure or operational technology. The conversation with Firevault begins with what matters to the organisation.

1 / 6

An analogy for a collaboration, not a claim that these services are automatically integrated. Scope, dependencies, clean-copy validation and recovery decisions are agreed with the customer. No guaranteed recovery time.

British-founded. Global ambition.

We are only getting started.

Firevault is a UK cyber resilience company, offering data protection and storage through Offline Secure Storage® and network evolution and rapid protection through Control by Firevault. We are proud to have taken our ideas from architecture and testing into live customer environments, while building the partnerships, technology and expertise needed for what comes next.

Firevault Bunkers operate across Europe, including the United Kingdom, with United States and Middle East sites next. Jurisdiction is agreed in writing at onboarding.

Explore Firevault Bunkers

No single technology removes every risk. Good cybersecurity, strong governance and responsible people will always matter. But organisations deserve physical control over the connections and assets that matter most.

Disconnect to Protect®

Sometimes, the strongest defence is removing the connection altogether.

The future of protection is physical.
Protect what matters. Control what moves.