Professionally managed facilities
Bunkers are selected for concurrently maintainable infrastructure, controlled operations and layered security rather than ordinary office storage.

 Physical SecurityOne of four physical principles
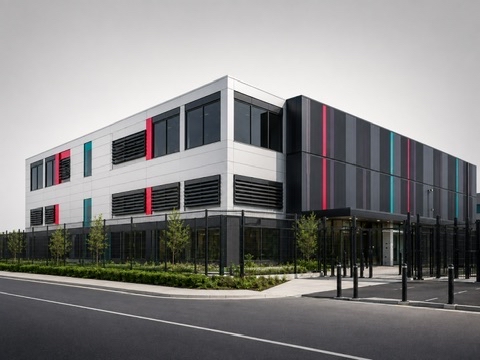
Your dedicated hardware is housed inside carefully selected, professionally managed Firevault Bunkers with layered perimeter, access, power and environmental controls around the equipment.
Vaults from £360 a month inc VAT. 36-month commitment, first payment at checkout.
As featured in





Why it matters
Disconnecting a network route removes remote exposure. The Bunker protects the hardware itself against unauthorised entry, power interruption, environmental events, fire and unrecorded handling.
Controlled approaches, monitored entrances and restricted internal zones place several barriers between the public and the racks.
Three-factor authentication, including biometric identification, ties physical entry to a verified person.
24/7 monitoring and a complete audit trail record access and protect the operating environment.
Layered site protectionPhysical Security
How it works
Physical security works in layers, from the site boundary to the specific rack and every authorised intervention.
Step 1 of 5
Firevault allocates a Bunker by default, or confirms a requested jurisdiction in writing where required.
Step 2 of 5
Fencing, surveillance and controlled vehicle and pedestrian routes protect the facility boundary.
Step 3 of 5
Authorised personnel pass three-factor access controls, including biometric identification, before entering restricted areas.
Step 4 of 5
Redundant utility feeds, uninterruptible power, generator backup, controlled cooling and monitored alarms protect the commissioned hardware.
Step 5 of 5
Entry and operational handling create an audit trail that supports investigation and assurance.
Offline by default: the hardware is physically disconnected outside authorised sessions.
Inside the security model
Bunkers are selected for concurrently maintainable infrastructure, controlled operations and layered security rather than ordinary office storage.
The site, approaches and controlled areas remain under continuous security oversight.
Physical entry includes a factor tied to the authorised person, not only something they know or carry.
Passing the outer entrance does not grant unrestricted movement through the facility.
Redundant power paths, UPS and generator backup help maintain service through utility interruption.
Purpose-designed cooling, temperature monitoring and fire detection protect equipment operating conditions.
Firevault allocates a Bunker by default, or confirms a requested jurisdiction in writing where required.
What it does not replace
Physical security answers where and how the hardware is protected. It does not replace dedicated media, customer assignment or control of the network route.
Across every instance
Hosted hardware sits inside a Firevault Bunker. Storage and Enterprise can also be designed for your premises.
Choose your Vault
Pick the capacity. File Manager, File Share, Vault Buddy and Vault Spare come with every size.
Dedicated physical capacity
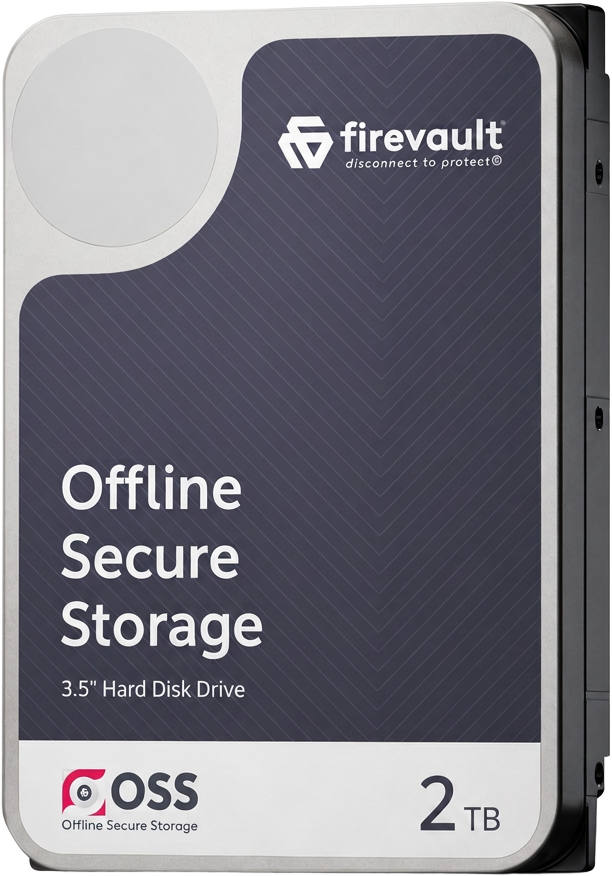 2TB
Contracts, company records, financial evidence and the client documents a small business cannot replace.
£360per month inc VAT
£300 a month ex VAT, 36-month commitment
Configure 2TBAsk a questionDedicated physical capacity
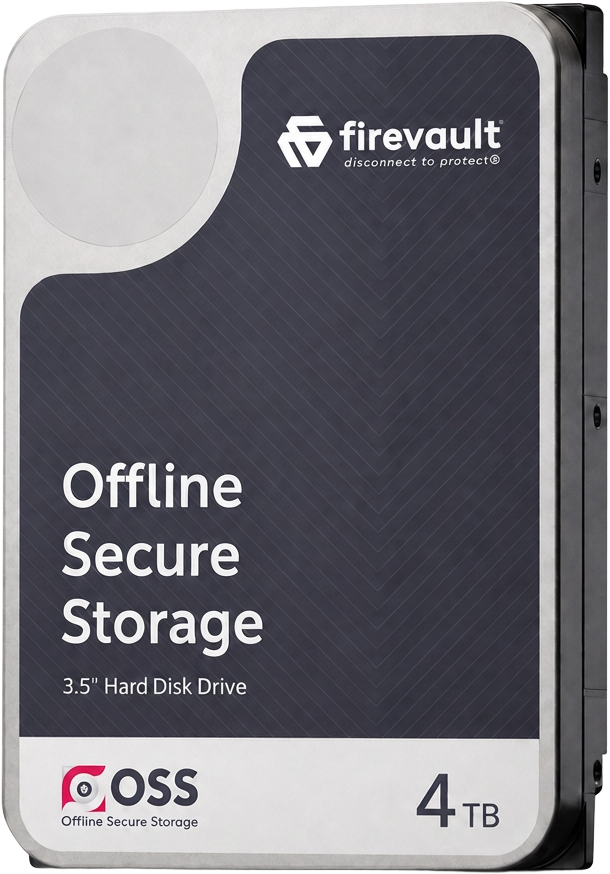 4TB
For growing businesses and professionals, with meaningful room to expand.
£480per month inc VAT
£400 a month ex VAT, 36-month commitment
Configure 4TBAsk a questionDedicated physical capacity
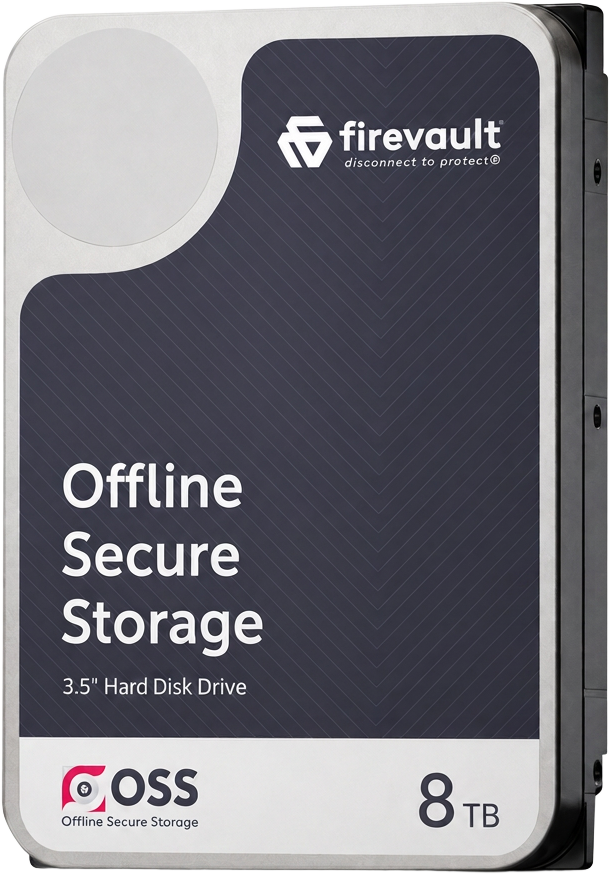 8TB
Substantial archives, creative work and records built up over many years. Adds a dedicated account manager.
£600per month inc VAT
£500 a month ex VAT, 36-month commitment
Configure 8TBAsk a questionEvery Vault belongs to one user. 36-month commitment, first payment at checkout.
In every OSS instance
File Manager, File Share, Vault Buddy and Vault Spare come with every OSS instance. Here are the other three.
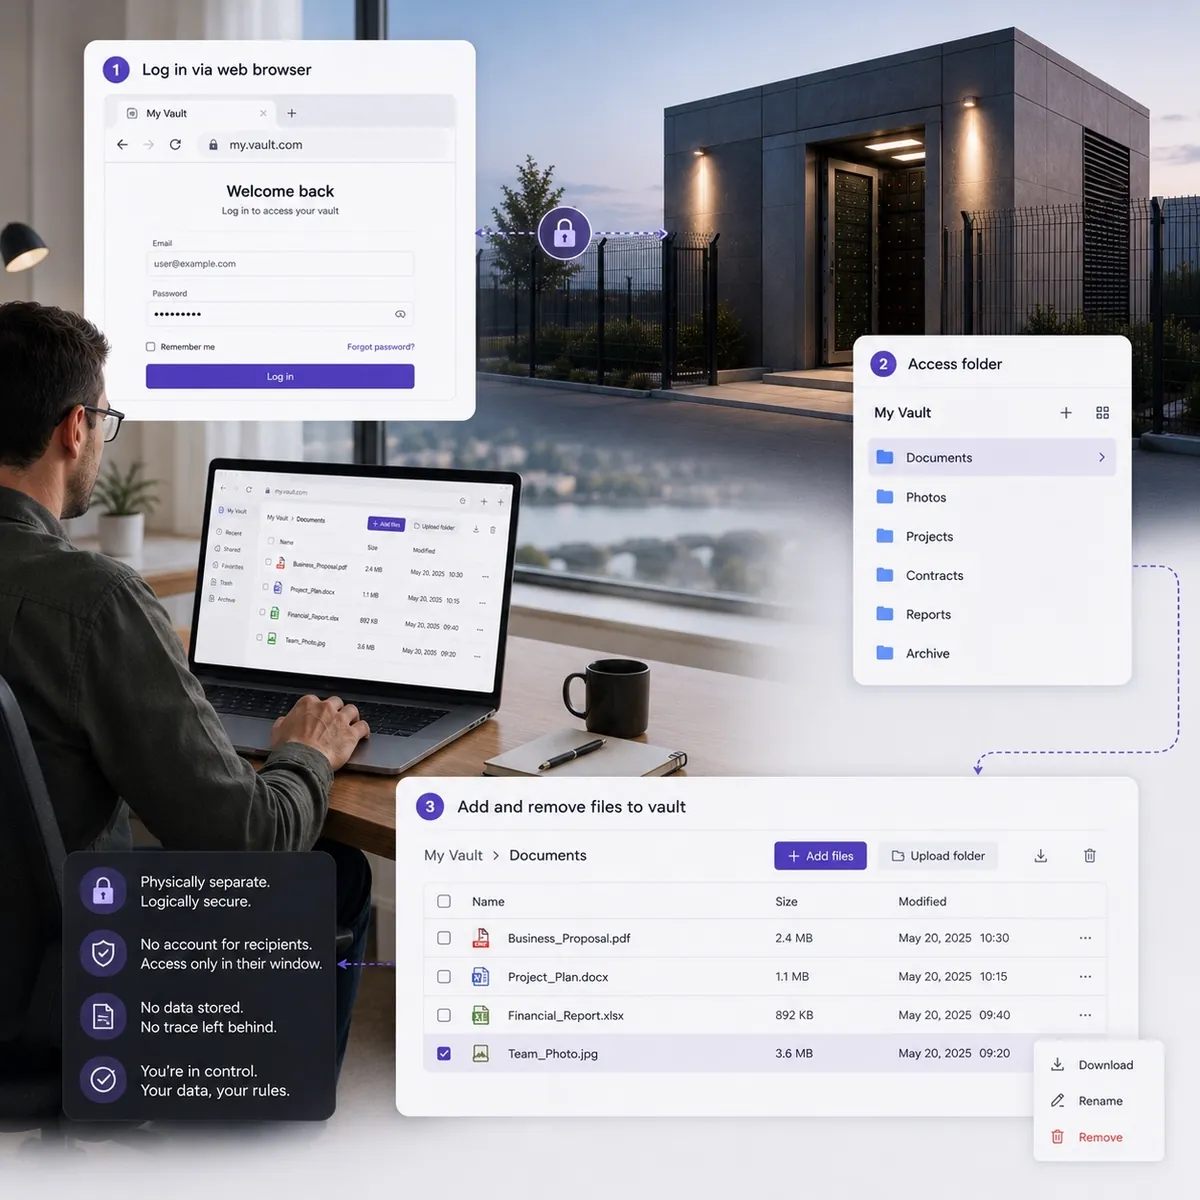 File ManagerUpload, overwrite, create folders and share from any modern browser during an authorised window. Nothing to install.Explore File Manager
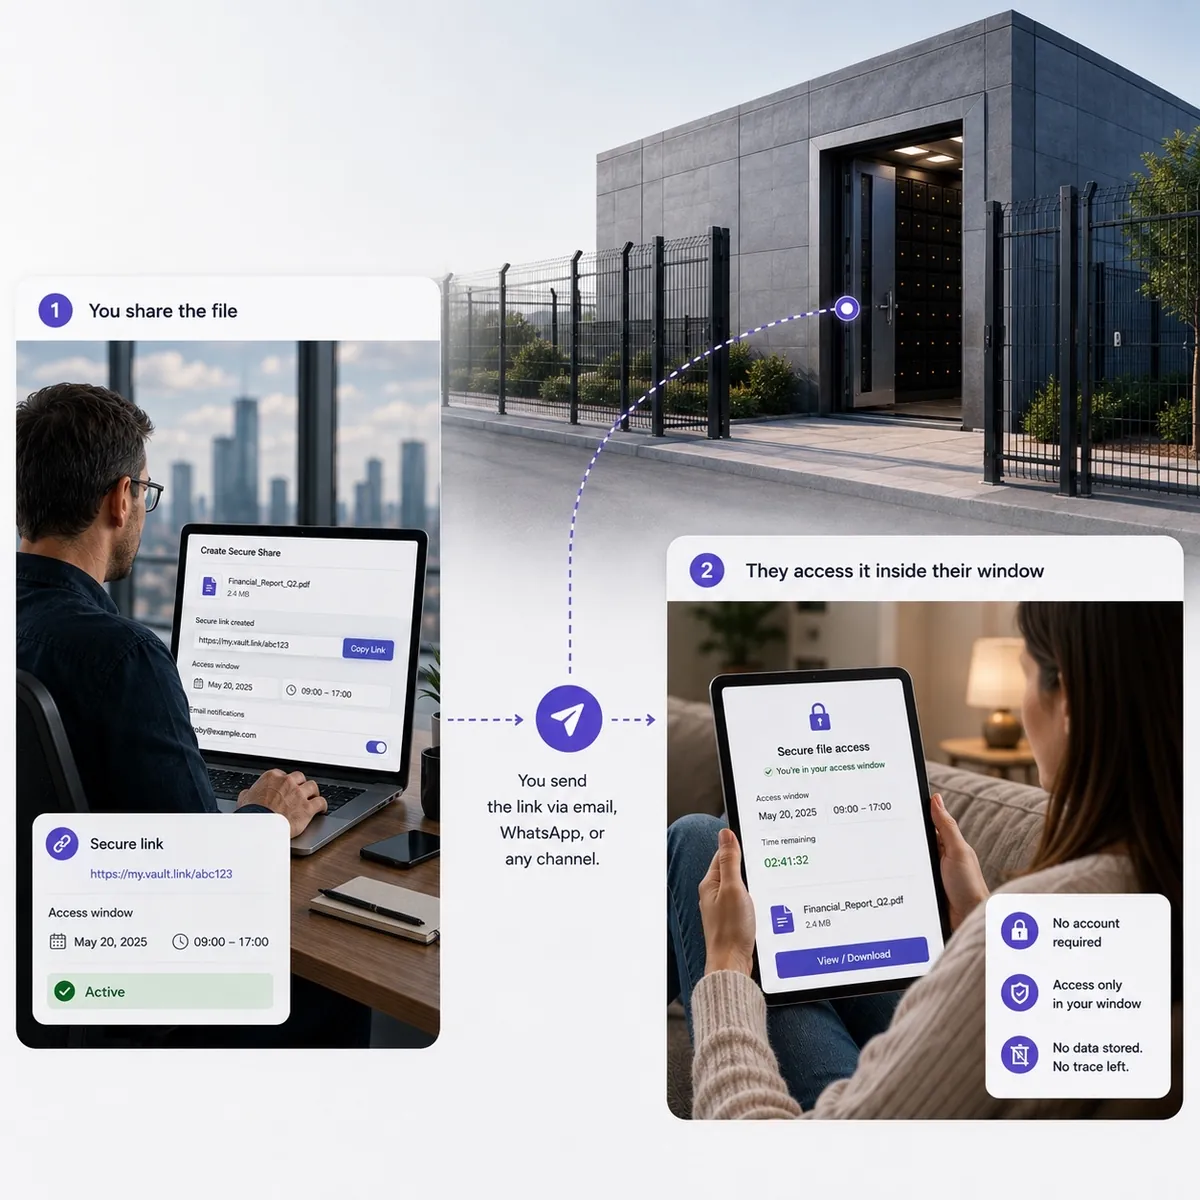 File ShareA time-boxed, password-protected link to a record in your Vault, withdrawn the moment the exchange is done.Explore File Share
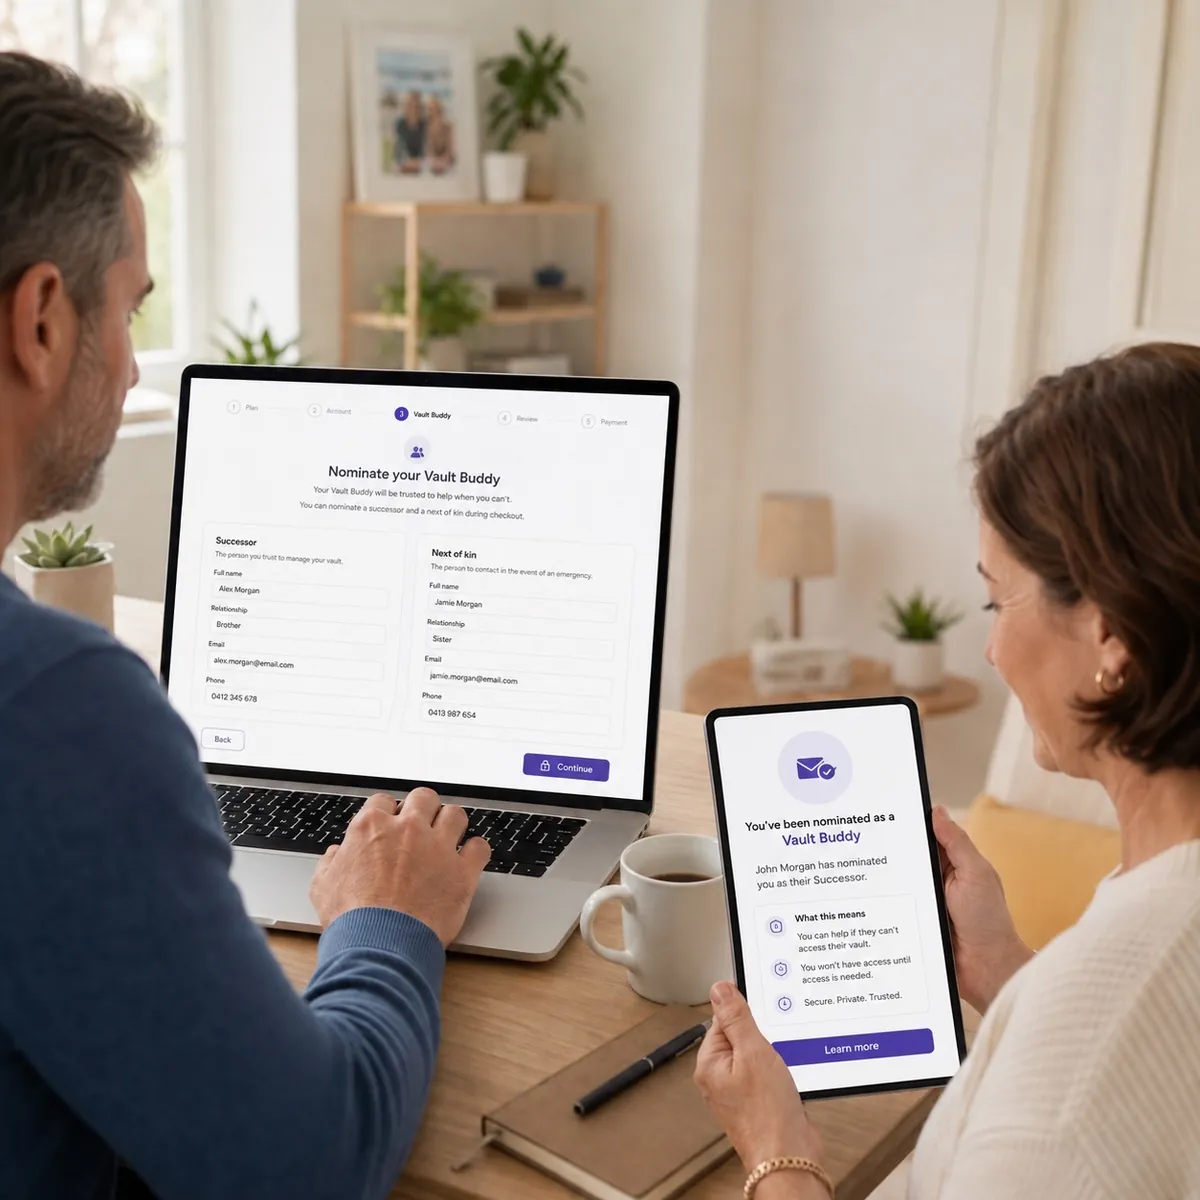 Vault BuddyNominate who should be able to reach your Vault. Released only on documentary evidence and verified identity.Explore Vault Buddy
Questions
Europe is live, including the UK. The US and Middle East are next.
Firevault allocates a Bunker by default, or confirms a requested jurisdiction in writing where required.
Authorised entry requires three independent checks, including biometric identification, before a person can reach restricted areas.
Yes. Security and critical environmental conditions are monitored 24 hours a day, every day.
The selected facilities use resilient power architecture, including uninterruptible power and backup generation, alongside monitored cooling and environmental systems.
No. Physical facility access does not provide customer credentials or create a network route to the data. Those controls remain separate.
No. It works with dedicated physical storage, defined ownership and physical control of connectivity. The four principles are designed to operate together.
 Disconnect to Protect®
Choose your Vault capacity and let Firevault place it inside the physical and operational controls of a Firevault Bunker.