RAID 1 mirroring
Each Vault uses dedicated physical drives, so your files are held on both disks.
Physical storage
 SecurityHow your copy is protected
Physical disconnection, verified identity, time-limited sessions and a protected Bunker, with a record of every session.
As featured in






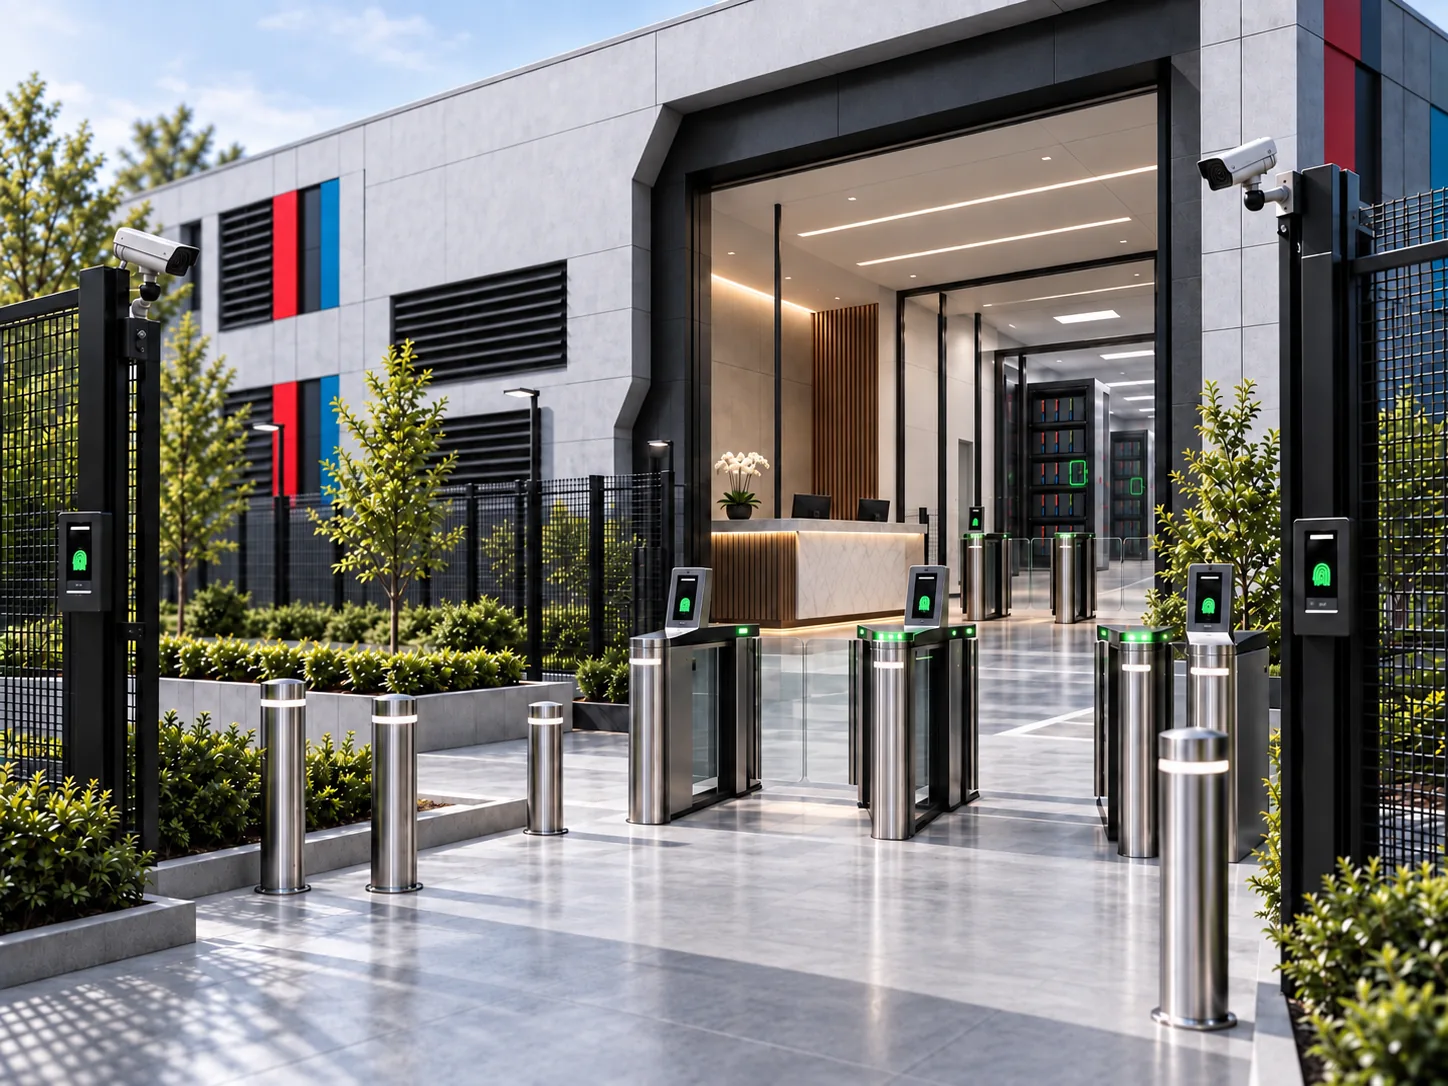
Three independent entry checksIncluding biometrics
24/7 monitoringA Tier 3 data centre
How it is protected
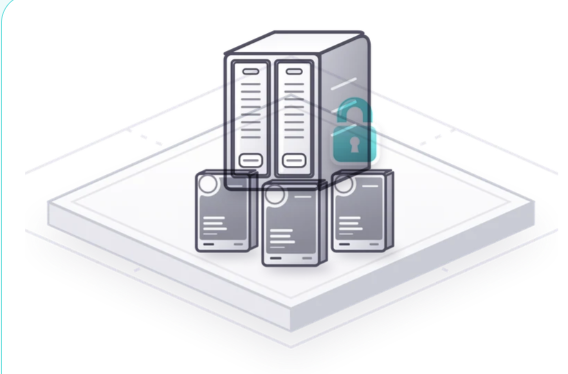
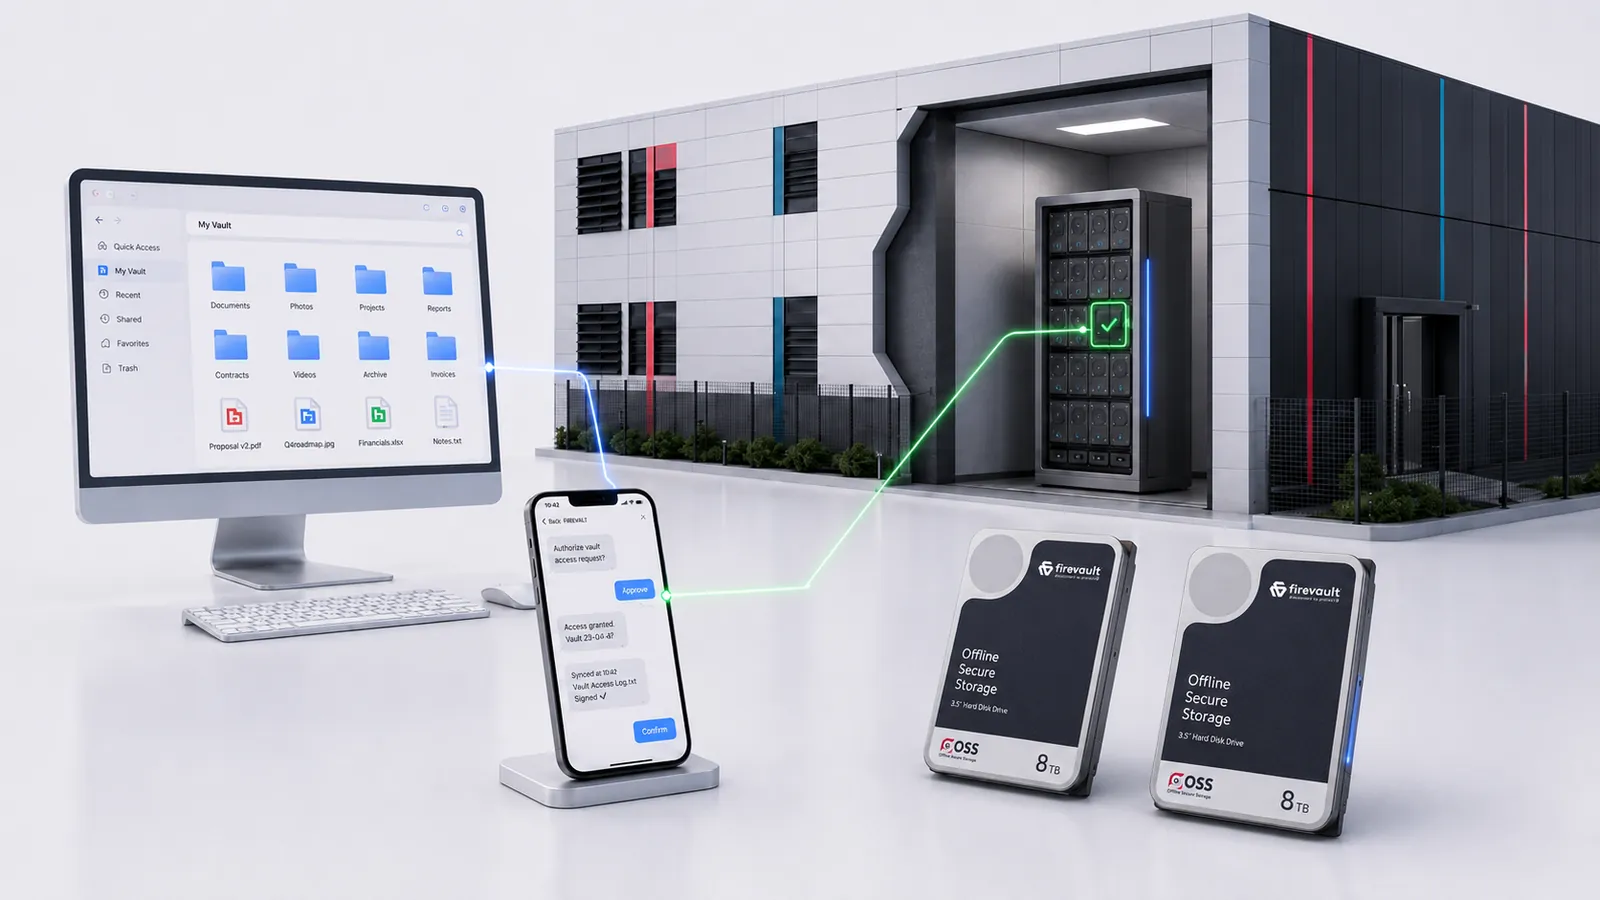
No standing network path. A route exists only for an authorised session, and it is removed when the session ends.
Organisation and identity checks at onboarding, in line with KYC and AML practice, then multi-factor authentication on every session.
Sessions are time-limited, up to 120 minutes, and every one is logged.
A professionally managed data centre in our international estate, with three independent entry checks and 24/7 monitoring.
No path while it is closed
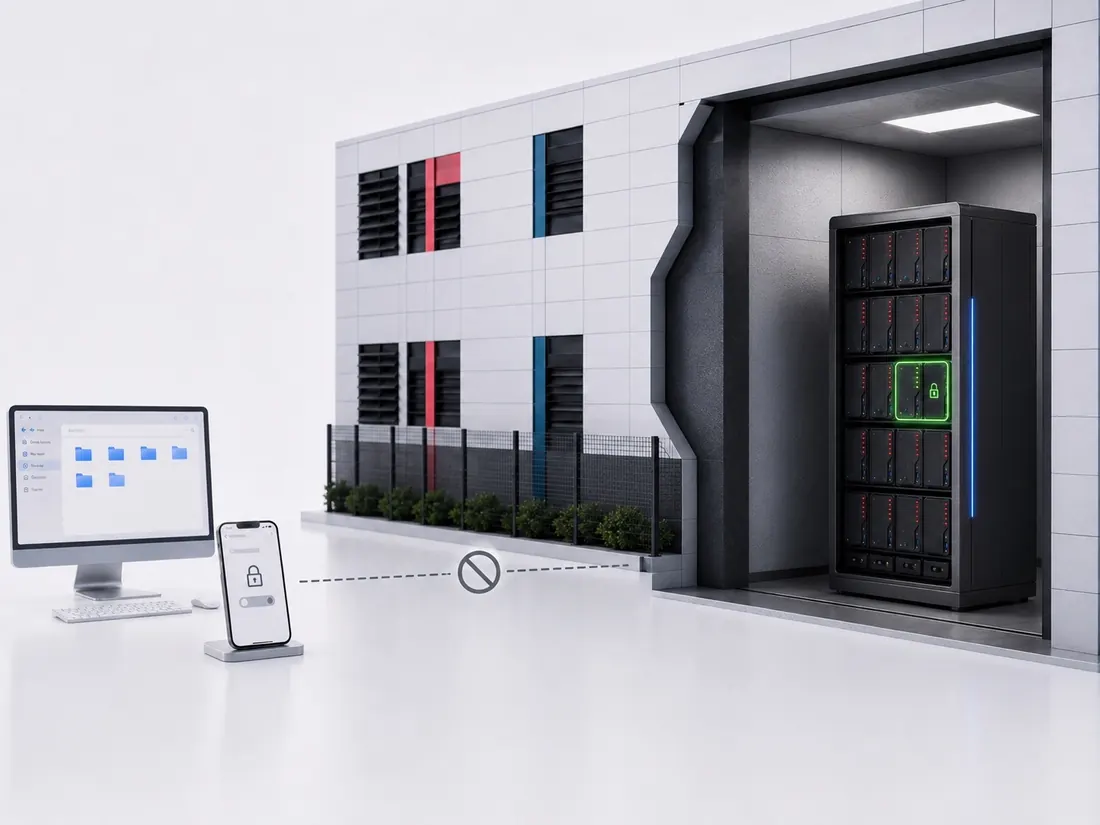
Hardware lifecycle
The organisation and the authorised user are verified before anything is provisioned.
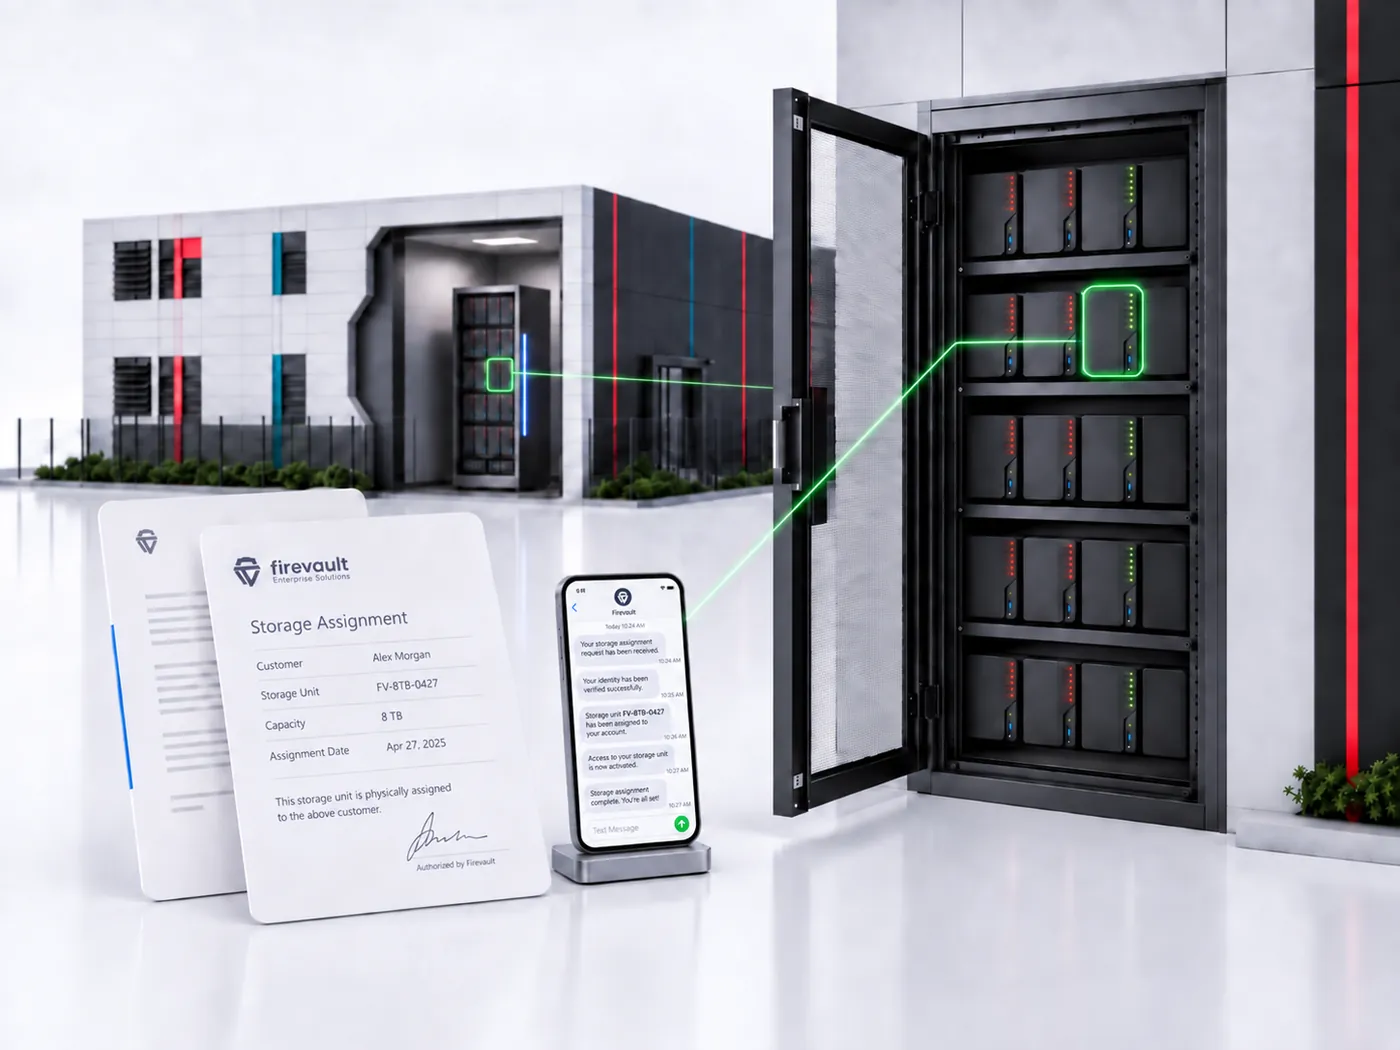
Dedicated hardware is assigned to one customer and recorded.
RAID 1 mirroring, with Vault Spare for hardware continuity.
At the end of the term: renew, retrieve the drive, or destroy it to certificate.
Assurance
We map our controls to the outcomes your auditors test. We do not claim certification on your behalf.
Your organisation remains responsible for how applicable frameworks are implemented.
Continuity
Each Vault uses dedicated physical drives, so your files are held on both disks.
Physical storage
Already inside your Vault spare hardware for continuity.
Vault Spare
A nominated person who has no access until a qualifying event is evidenced and their identity is verified.
Vault BuddyQuestions
On dedicated hardware in a Firevault Bunker, a professionally managed data centre in our international estate. For security, we do not publish Bunker locations.
We are the infrastructure provider and we do not know your credentials. Sessions are opened by you, verified with MFA, and logged.
Every connection, disconnection and identity verification, so you can show a physical control and a record of each session to auditors and insurers.
Each Vault uses dedicated physical drives with RAID 1 mirroring, so your files are held on both disks. Vault Spare adds pre-provisioned spare hardware for continuity.
Confirm current Cyber Essentials Plus status, certificate scope and validity with Firevault before relying on it. Offline Secure Storage® can help support GDPR, NIS2, ISO 27001 and NIST CSF obligations.
You can renew month by month, retrieve the physical drive, or have it destroyed to certificate.
Need our security answers for a supplier questionnaire? Tell us what you need and we will send it.