Resilience
Gold Copy Backups
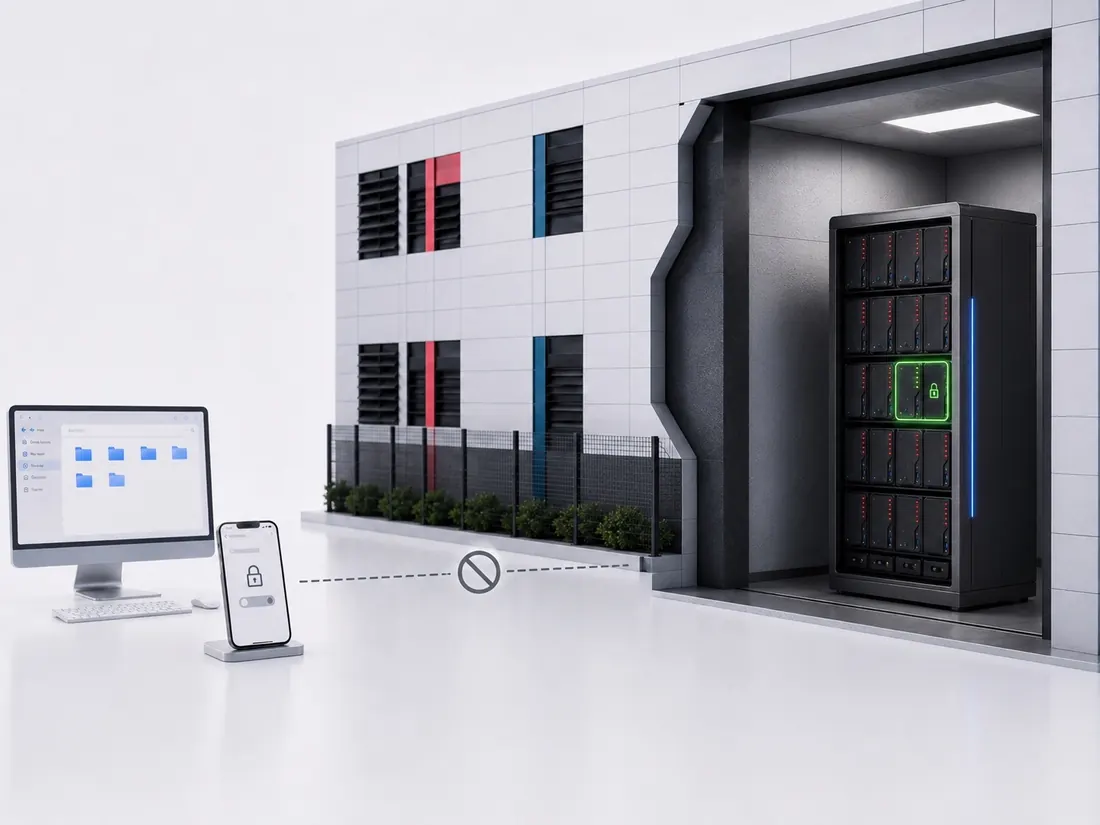
Hold gold copies off the network the attack runs on.
Explore
 Use case · Operational technology
PLC programs, HMI projects, SCADA configurations and safety-case evidence held on hardware that is physically disconnected, so a line can be rebuilt after an incident.
As featured in





The problem
Operational technology recovery fails when the only copies of PLC programs, HMI projects, SCADA configurations and engineering records sit on connected infrastructure. When IT ransomware bridges across to the OT estate, those engineering shares are encrypted alongside production. Without an intact master copy, plant teams struggle to prove the safety case is unchanged, to rebuild a line at speed, or to give regulators the evidence they need.

How it plays out
One realistic sequence of events, then the controls that break it. Switch between the two, or play it through.
Step 1 of 2
A manufacturer is hit by ransomware on a Friday evening. The intrusion starts in IT, reaches the engineering jump host, and encrypts the shared drive holding PLC backups, HMI projects and SCADA configurations. The on-site NAS sits on the same network and is encrypted too.
By Monday the line is still down, the safety officer cannot evidence the last validated state of the controllers, and the insurer is asking for the document trail that no longer exists.
Step 2 of 2
Golden images and configurations: PLC programs, HMI projects and SCADA configurations held on physically disconnected media, with per-asset versioning so engineers restore the right build for the right controller.
OT ransomware recovery: offline by default and reachable per session, so recovery teams pull only what they need, through a clean-room restore path kept apart from any compromised network.
Safety-case evidence custody: validation records, change logs and HAZOP outputs preserved offline, so the safety case survives the incident.
NIS2 and CAF evidence held in tamper-evident storage, ready to hand to auditors and regulators after an event.
An illustrative scenario.
The outcome
With golden images, engineering data and safety-case evidence held in Firevault Offline Secure Storage®, the restart can begin from a validated master copy, and the safety officer and insurer get the document trail they ask for.
The data sits on physical Firevault hardware, not a shared cloud tenancy.
Offline by default. There is no standing network path in or out of the vault.
Access opens on your instruction, with identity verified and every session logged.
Held in a Firevault Bunker. Firevault provisions the location.
Choose your Vault and check out in minutes. Dedicated hardware, identity-locked to you, physically disconnected when closed. From £360 a month including VAT. 36-month commitment. First payment at checkout.