
Incident 1
Capita: £14m ICO fine.
The ICO fined outsourcer Capita £14 million over a 2023 cyber attack that affected the personal data of more than 6 million people. ICO, October 2025.
Answered byRecords off connected infrastructure
 OSS® for financial services
Financial services face extraordinary regulatory scrutiny and cyber risk. Offline Secure Storage (OSS) provides physical disconnection for your most sensitive financial data.
As featured in





The reality
Every incident here is a matter of public record. Each one involved data that was reachable from a live network at the moment of compromise.
Financial records are removed from always-connected infrastructure and placed on hardware with no network connection while it is closed.
Stolen credentials alone do not open hardware that is physically disconnected.
Every session is identity-verified and logged, which can help support FCA, PRA and DORA reporting.
Incident 1
The ICO fined outsourcer Capita £14 million over a 2023 cyber attack that affected the personal data of more than 6 million people. ICO, October 2025.
Answered byRecords off connected infrastructureIncident 2
The ICO fined LastPass £1.2 million after a 2022 breach in which attackers took encrypted password vaults belonging to up to 1.6 million UK users. ICO, December 2025.
Incident 3
Attackers took personal data belonging to all 6.5 million Co-op members, including names and contact details. Co-op, July 2025.

How OSS helps
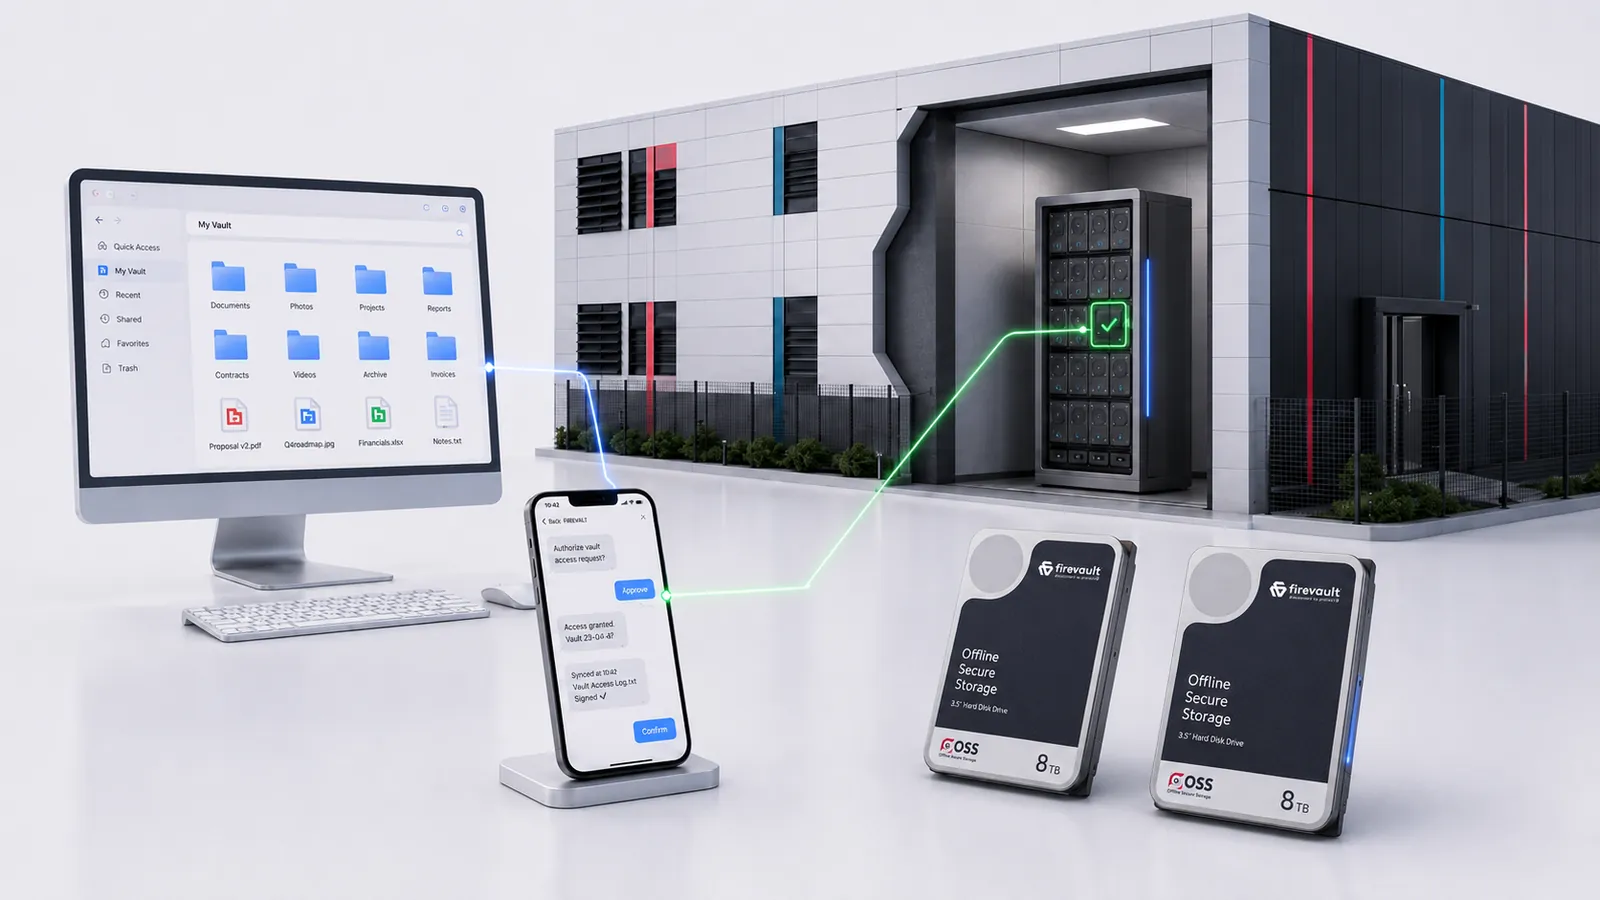
Customer records, transaction archives and regulatory files are taken off always-connected infrastructure and written to dedicated RAID 1 drives inside a Firevault Bunker. When authorised staff need access, a physical connection is created after identity verification. When the session ends, the drives disconnect.
Step 1 of 3
Customer records, transaction archives and regulatory files are taken off always-connected infrastructure and written to dedicated RAID 1 drives inside a Firevault Bunker.
No cloud. No shared portal.
Step 2 of 3
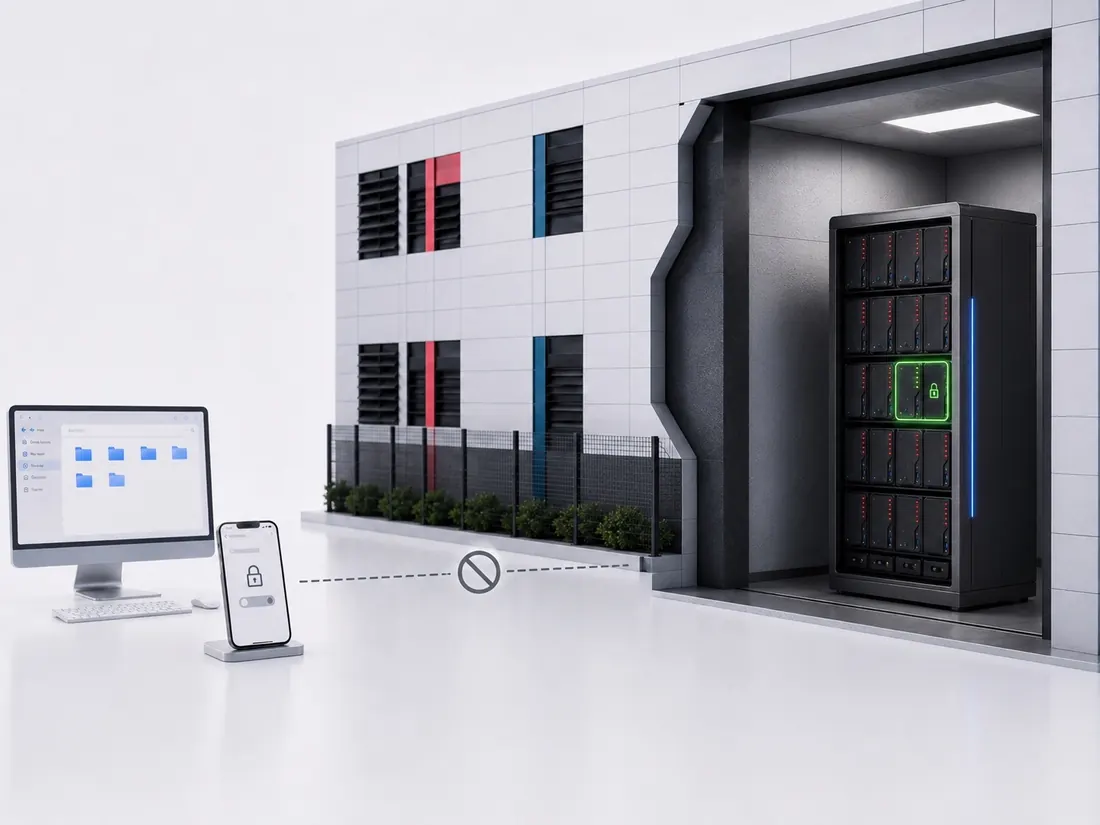
While they are closed, those drives have no internet connection, no IP address and no API.
Stolen credentials alone do not open hardware that is physically disconnected.
Step 3 of 3
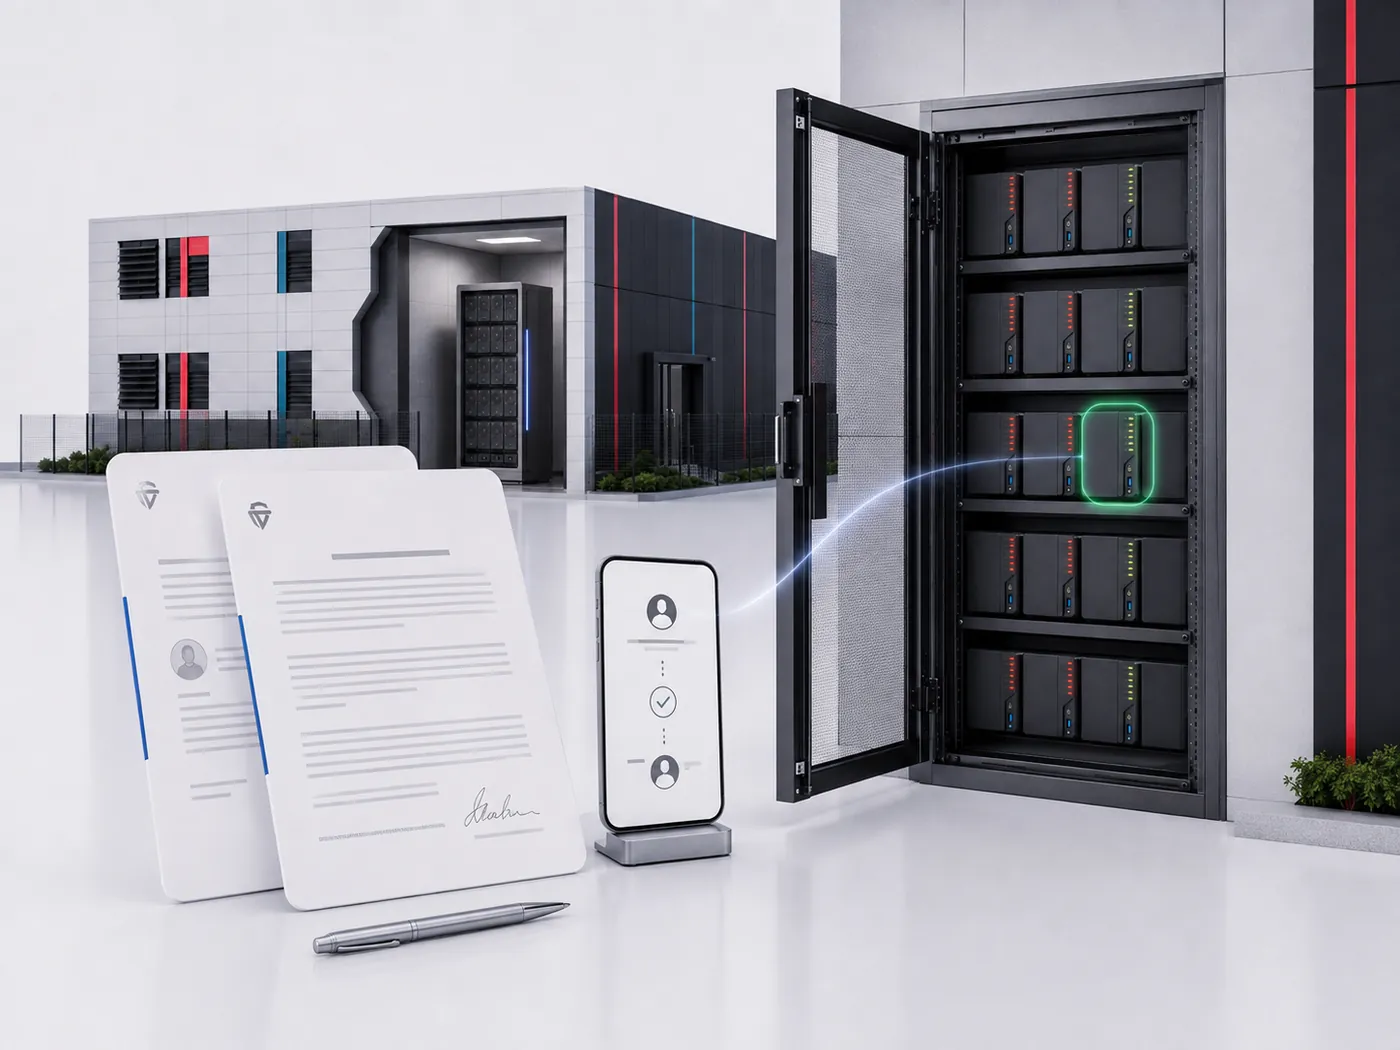
When authorised staff need access, a physical connection is created after identity verification.
When the session ends, the drives disconnect, and every session is logged.
Illustration.
What the guidance says
UK and EU regimes both ask financial firms to evidence how critical services and their data survive disruption.
FCA operational resilience
Firms are expected to identify their important business services and show they can stay within impact tolerances through severe but plausible disruption.
FCA operational resilience
DORA Article 12
The Digital Operational Resilience Act sets backup and recovery requirements for financial entities, including backups that are physically and logically segregated from the source systems.
DORA on EUR-LexThe products
Every tier is the same physical principle at a different scale. Pick the access pattern that matches how your team works.
On-demand access, 24/7, to a digital safe deposit box. 2TB, 4TB or 8TB, from £360 a month inc VAT.
Deep cold storage for archived transaction records and compliance files accessed periodically. 300GB, with one nominated access day each week within a 12-hour window. £74.99 a month inc VAT, 36-month commitment.
Scalable offline capacity from 20TB upwards, designed with the solutions team around your requirement.
Vault
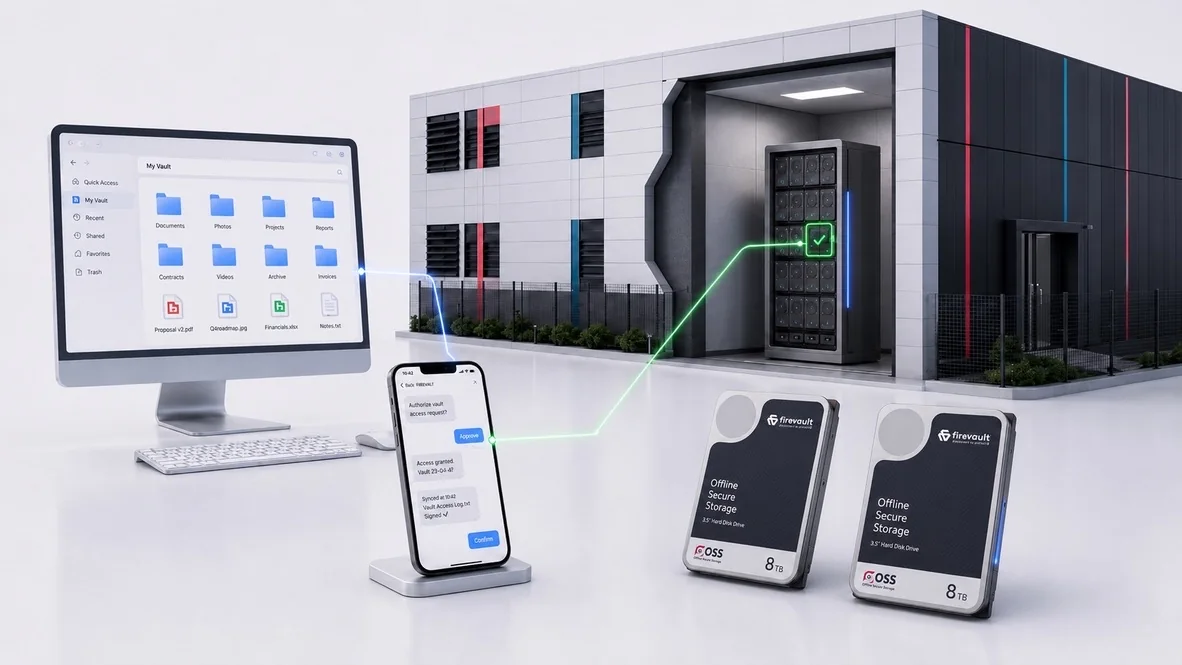
Open a session
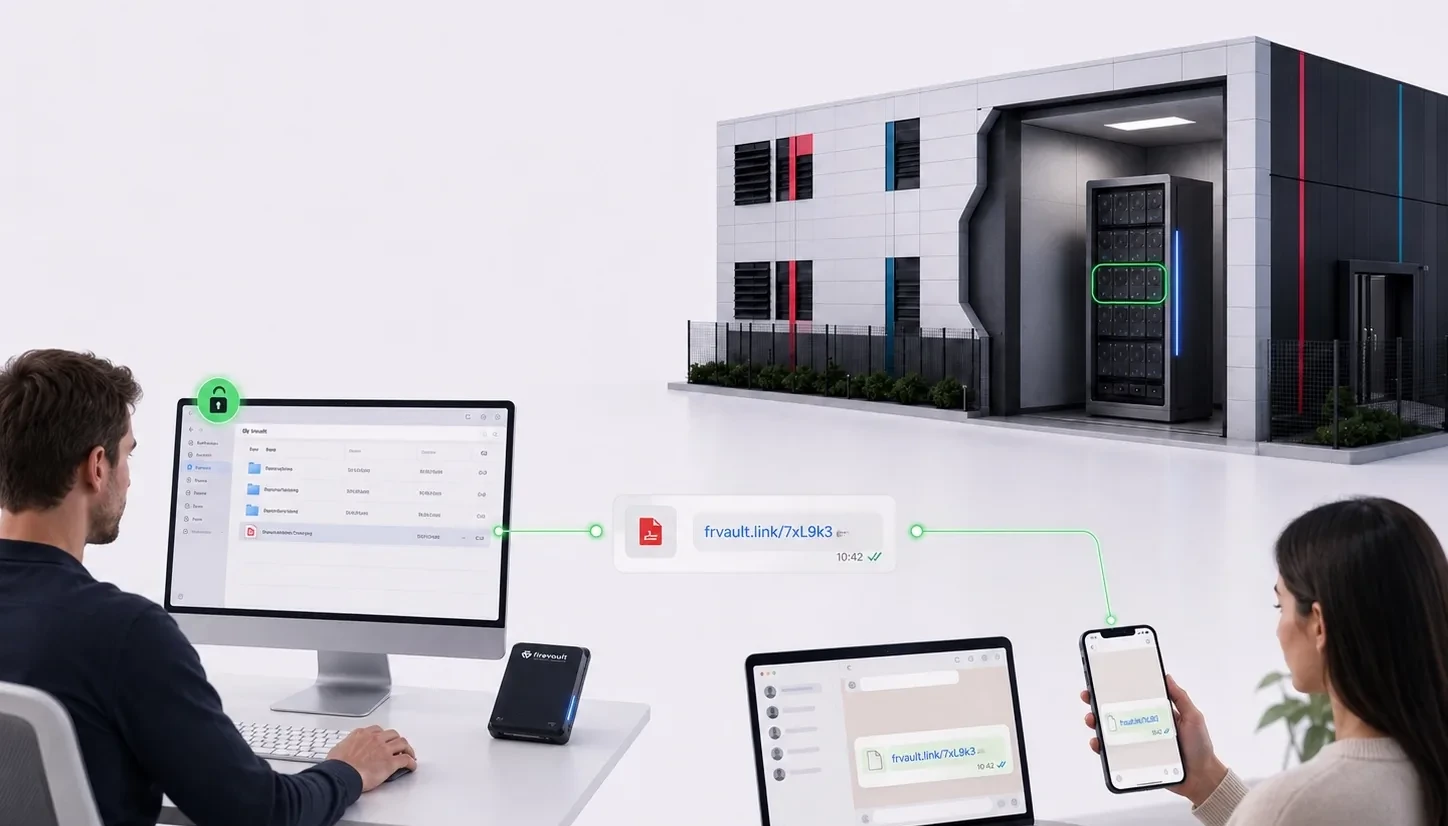
File Share
LUV

Storage
Use cases for financial services
The records that matter most, and the ones an attacker would most like to reach.
Transactions
Compliance
Onboarding
Accounts
Regulators
How to get started
Understand what you need to protect and how you operate.
Select your tier, capacity and access model.
Complete KYC/AML and set up multi-factor authentication.
Data ingestion, access policy activation and ongoing support.
Why Firevault
Every Offline Secure Storage® instance is built on the same four physical principles.
Offline Secure Storage instances are held on dedicated physical hard drives, not in S3 cloud buckets, shared storage pools or multi-tenant infrastructure. Your selected data is assigned to real hardware, with dedicated RAID 1 drives providing resilience.
Explore physical storage
Each Offline Secure Storage instance is allocated to a specific customer, with dedicated physical capacity and clearly defined ownership. Your data is not pooled, commingled or held within a shared storage estate.
Explore physical ownership
Access begins outside the normal network path. An authorised out-of-band command, such as SMS, controls the physical Layer 1 connection to your #OSS instance. When access is not required, that network path is physically disconnected.
Explore physical control
Your #OSS hardware is housed in carefully selected, professionally managed data centres with layered physical security, resilient power and environmental controls. Access is tightly controlled using three-factor authentication, including biometric identification, supported by 24/7 monitoring, restricted access zones and a complete audit trail.
Explore physical securityExplore more
Questions
Cloud storage keeps data permanently reachable over a network. Offline Secure Storage® holds selected data on dedicated hardware that is physically disconnected at the hardware level until you open a session.
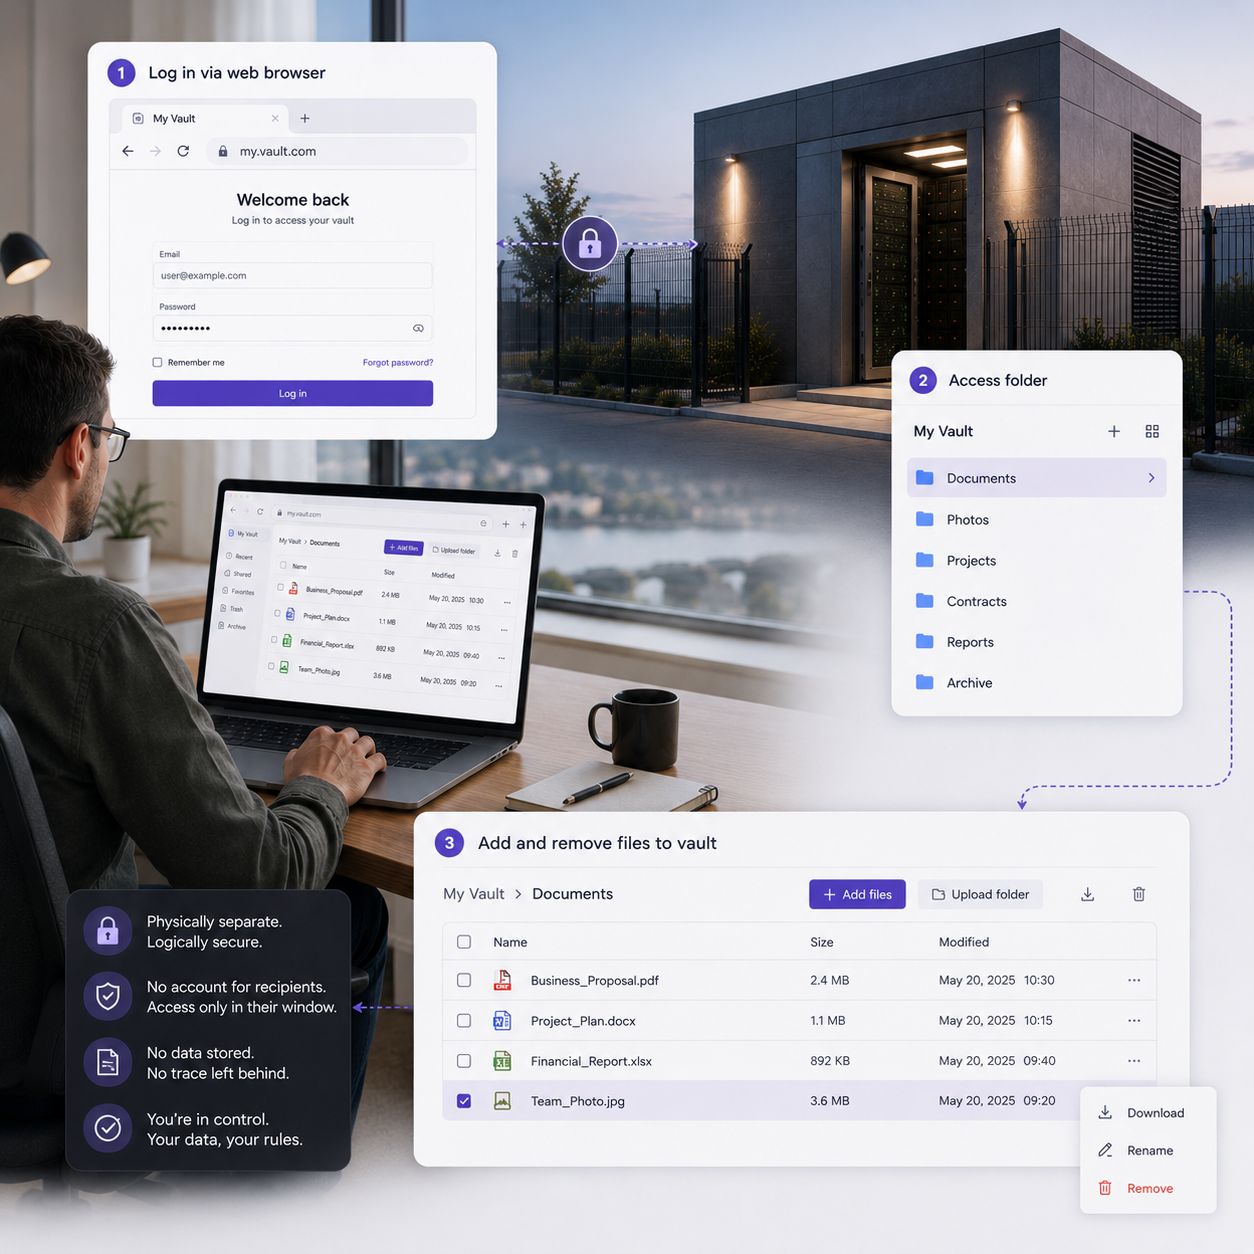
With a Vault, request a session at any time, 24/7, from your registered phone, sign in with your credentials and MFA, and work in File Share during a session of up to 120 minutes. LUV opens on your nominated access day each week, for 12 hours.
On dedicated hardware in a secure Firevault Bunker. For security, we do not publish Bunker locations.
Yes. Data is encrypted, and Firevault does not browse customer records. Your Vault is your own hardware, not a shared platform.

LUV from £74.99 and Vault from £360 a month, including VAT. 36-month commitment, first payment at checkout.